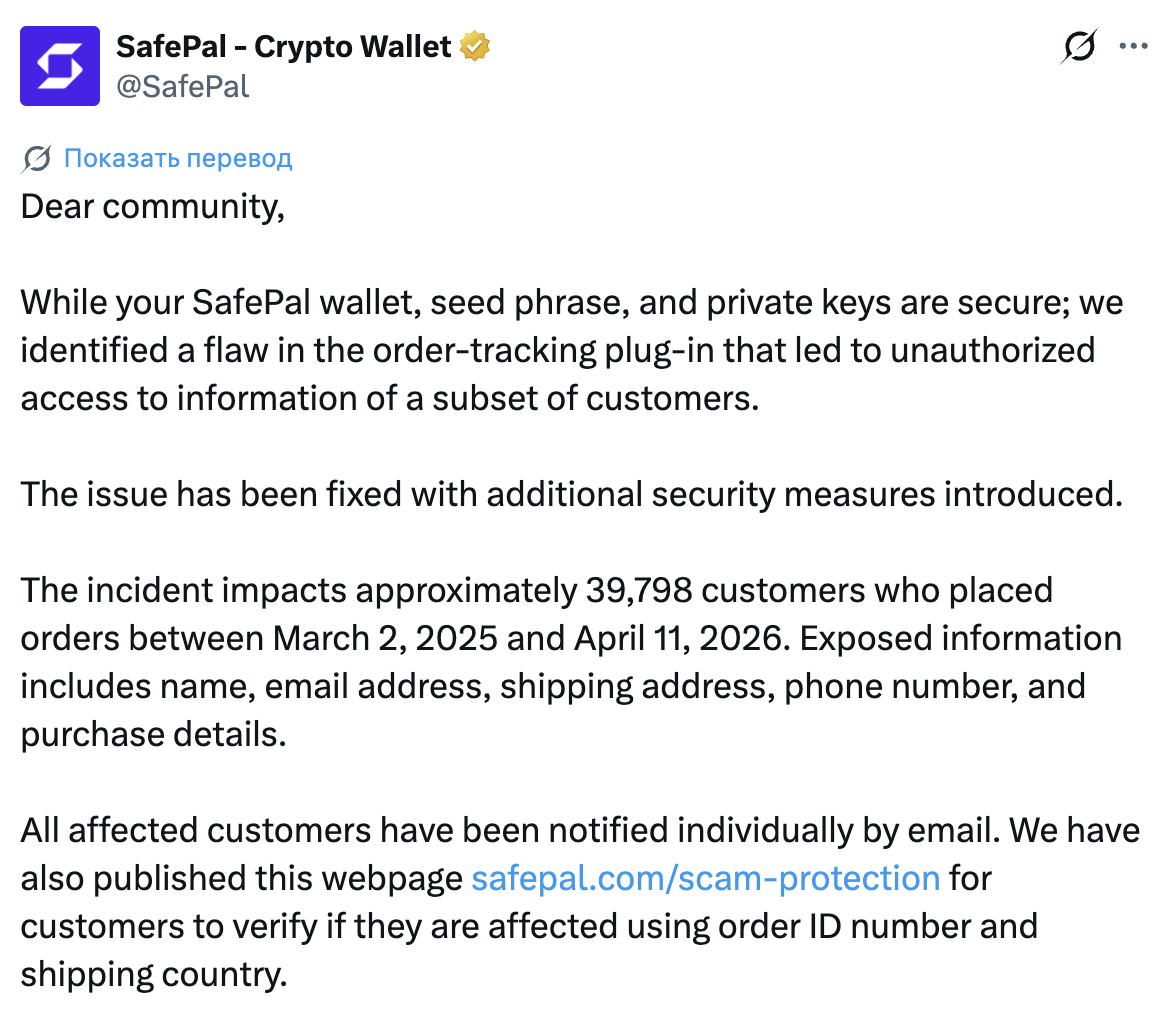
Crypto wallet maker SafePal has disclosed a breach of the personal data of 39,798 customers. The cause was an authorization vulnerability in the order-tracking plugin, through which outsiders could gain access to other people's data.
The company clarified that users' crypto assets, seed phrases, private keys and wallet passwords were not affected. The vulnerability has been fixed and additional security measures have been introduced.
What SafePal data became publicly accessible
The breach affected customers who placed orders from March 2, 2025 to April 11, 2026. Names, email addresses, physical shipping addresses, phone numbers and purchase details fell into the hands of outsiders.
The authorization vulnerability in the plugin worked on a simple scenario: the parcel-tracking system allowed one customer to see another's order and shipping address if they entered someone else's order number. No full-scale breach of the infrastructure was required.
At the same time, banking data, payment card numbers and government-issued IDs were not part of the incident. The main risk for those affected is targeted phishing attacks: attackers now know the address and phone number of a real hardware wallet owner.
How SafePal is responding to the breach
The company sent notifications to all 39,798 affected customers by email. To check whether a specific user was caught in the breach, it launched a verification tool on its site based on order number and shipping country.
SafePal brought in an independent third party to audit the fixes and check the order-processing system. The company also reduced the retention period for customers' personal data in the order-processing system to 90 days from the moment of collection.
Separately, SafePal took down more than 30 fraudulent sites and phishing links linked to this breach.
