On October 5, 2026, blockchain investigator ZachXBT published a 12-post thread describing how, in the spring of 2025, he posed as a client to infiltrate a Chinese group that, by his estimate, has laundered more than $1 billion for North Korea's Lazarus Group. He traded with one of its operators, known as Jimmy Green, put in $349,700 of his own money and matched the chats against on-chain data: Jimmy's address received gas from a wallet on Bybit's blacklist, and Jimmy himself told him in advance where the stolen money would move. The intelligence he gathered helped freeze part of the funds. Below is what exactly happened, what is confirmed on-chain and what remains the launderer's own words, and how this story connects to Huione, Poloniex and the recent Bitget hack.
On February 21, 2025, around $1.5 billion in ether was drained from the Bybit exchange. Five days later the FBI officially linked the attack to North Korea and called the activity TraderTraitor, the bureau's name for one of the strands of Lazarus Group. In the same statement, the FBI warned that the hackers were quickly converting the stolen assets into bitcoin and other assets, spreading them across thousands of addresses and would most likely cash them out into fiat.
THORChain, a protocol for swapping between blockchains without intermediaries, played a key role in this. After the Bybit hack it processed record volumes: on the day after the attack, daily swap volume exceeded half a billion dollars, and the protocol's operators refused to block transactions linked to Bybit.
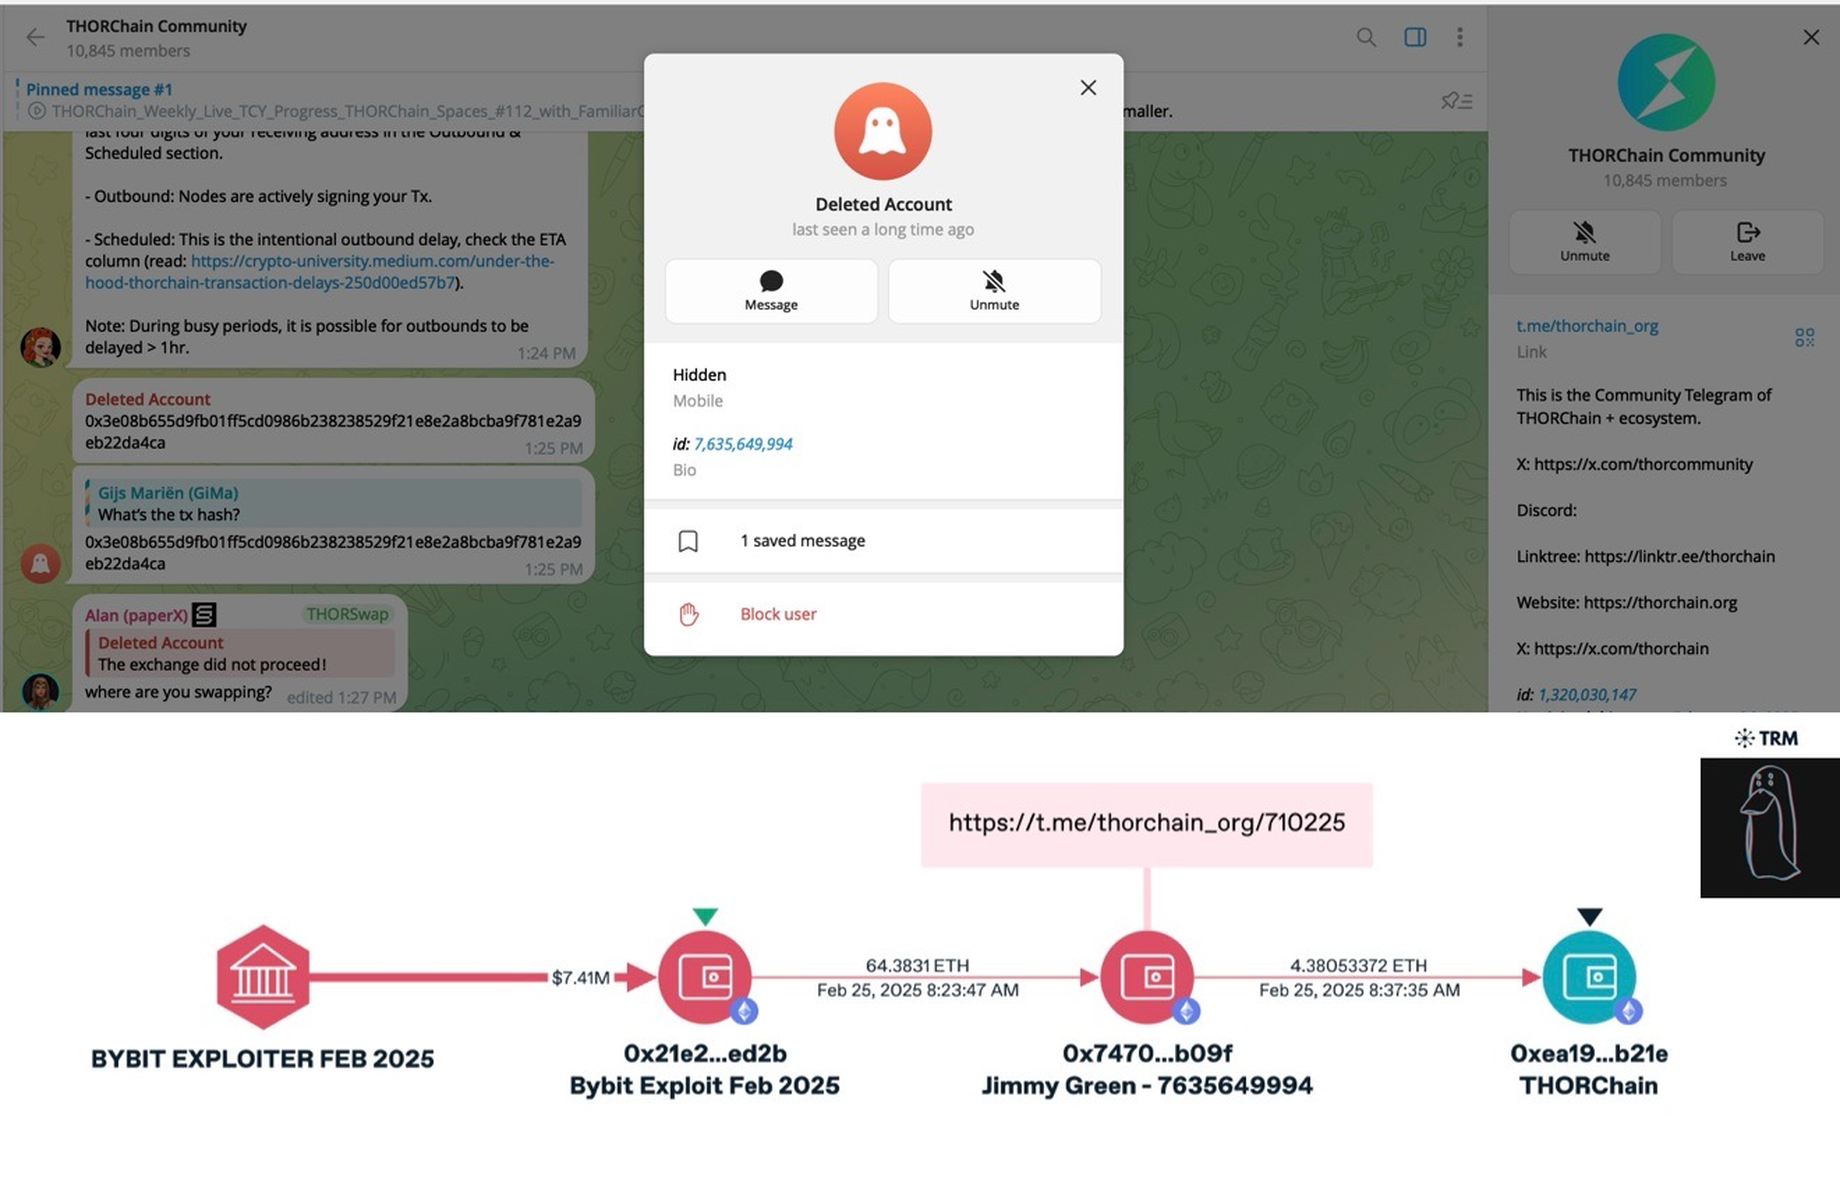
But swapping through a protocol is only the first step. Turning hundreds of millions into money that can actually be spent takes people: those who will take in «dirty» coins, return «clean» ones and find buyers. ZachXBT noticed that soon after the hack more than 15 accounts appeared in the public Telegram and Discord groups of services such as THORChain, complaining about stuck orders directly tied to the stolen funds. One of these accounts, in the THORChain community on Telegram, pasted a transaction hash and complained that the swap had not gone through. The account was later deleted, but its ID remained visible: 7635649994. It is the ID of Jimmy Green, the subject of this story.
The same picture repeated itself in September 2026. After the $387.5 million Bitget hack, ZachXBT showed how Chinese intermediaries laundering money for the alleged North Korean attackers were opening support tickets with services and asking staff to check «stuck» XRP-to-BTC swaps. He also linked one of them, using the handle lolo, to laundering after the $292 million Kelp DAO hack. The Jimmy Green thread follows the same line: it is an inside look at a network that serves North Korean hackers.
The largest crypto theft of the year: what happened to Bitget and who may have been behind the attack28 Eyl 2026Devamını oku
Who Jimmy Green is and what he offered
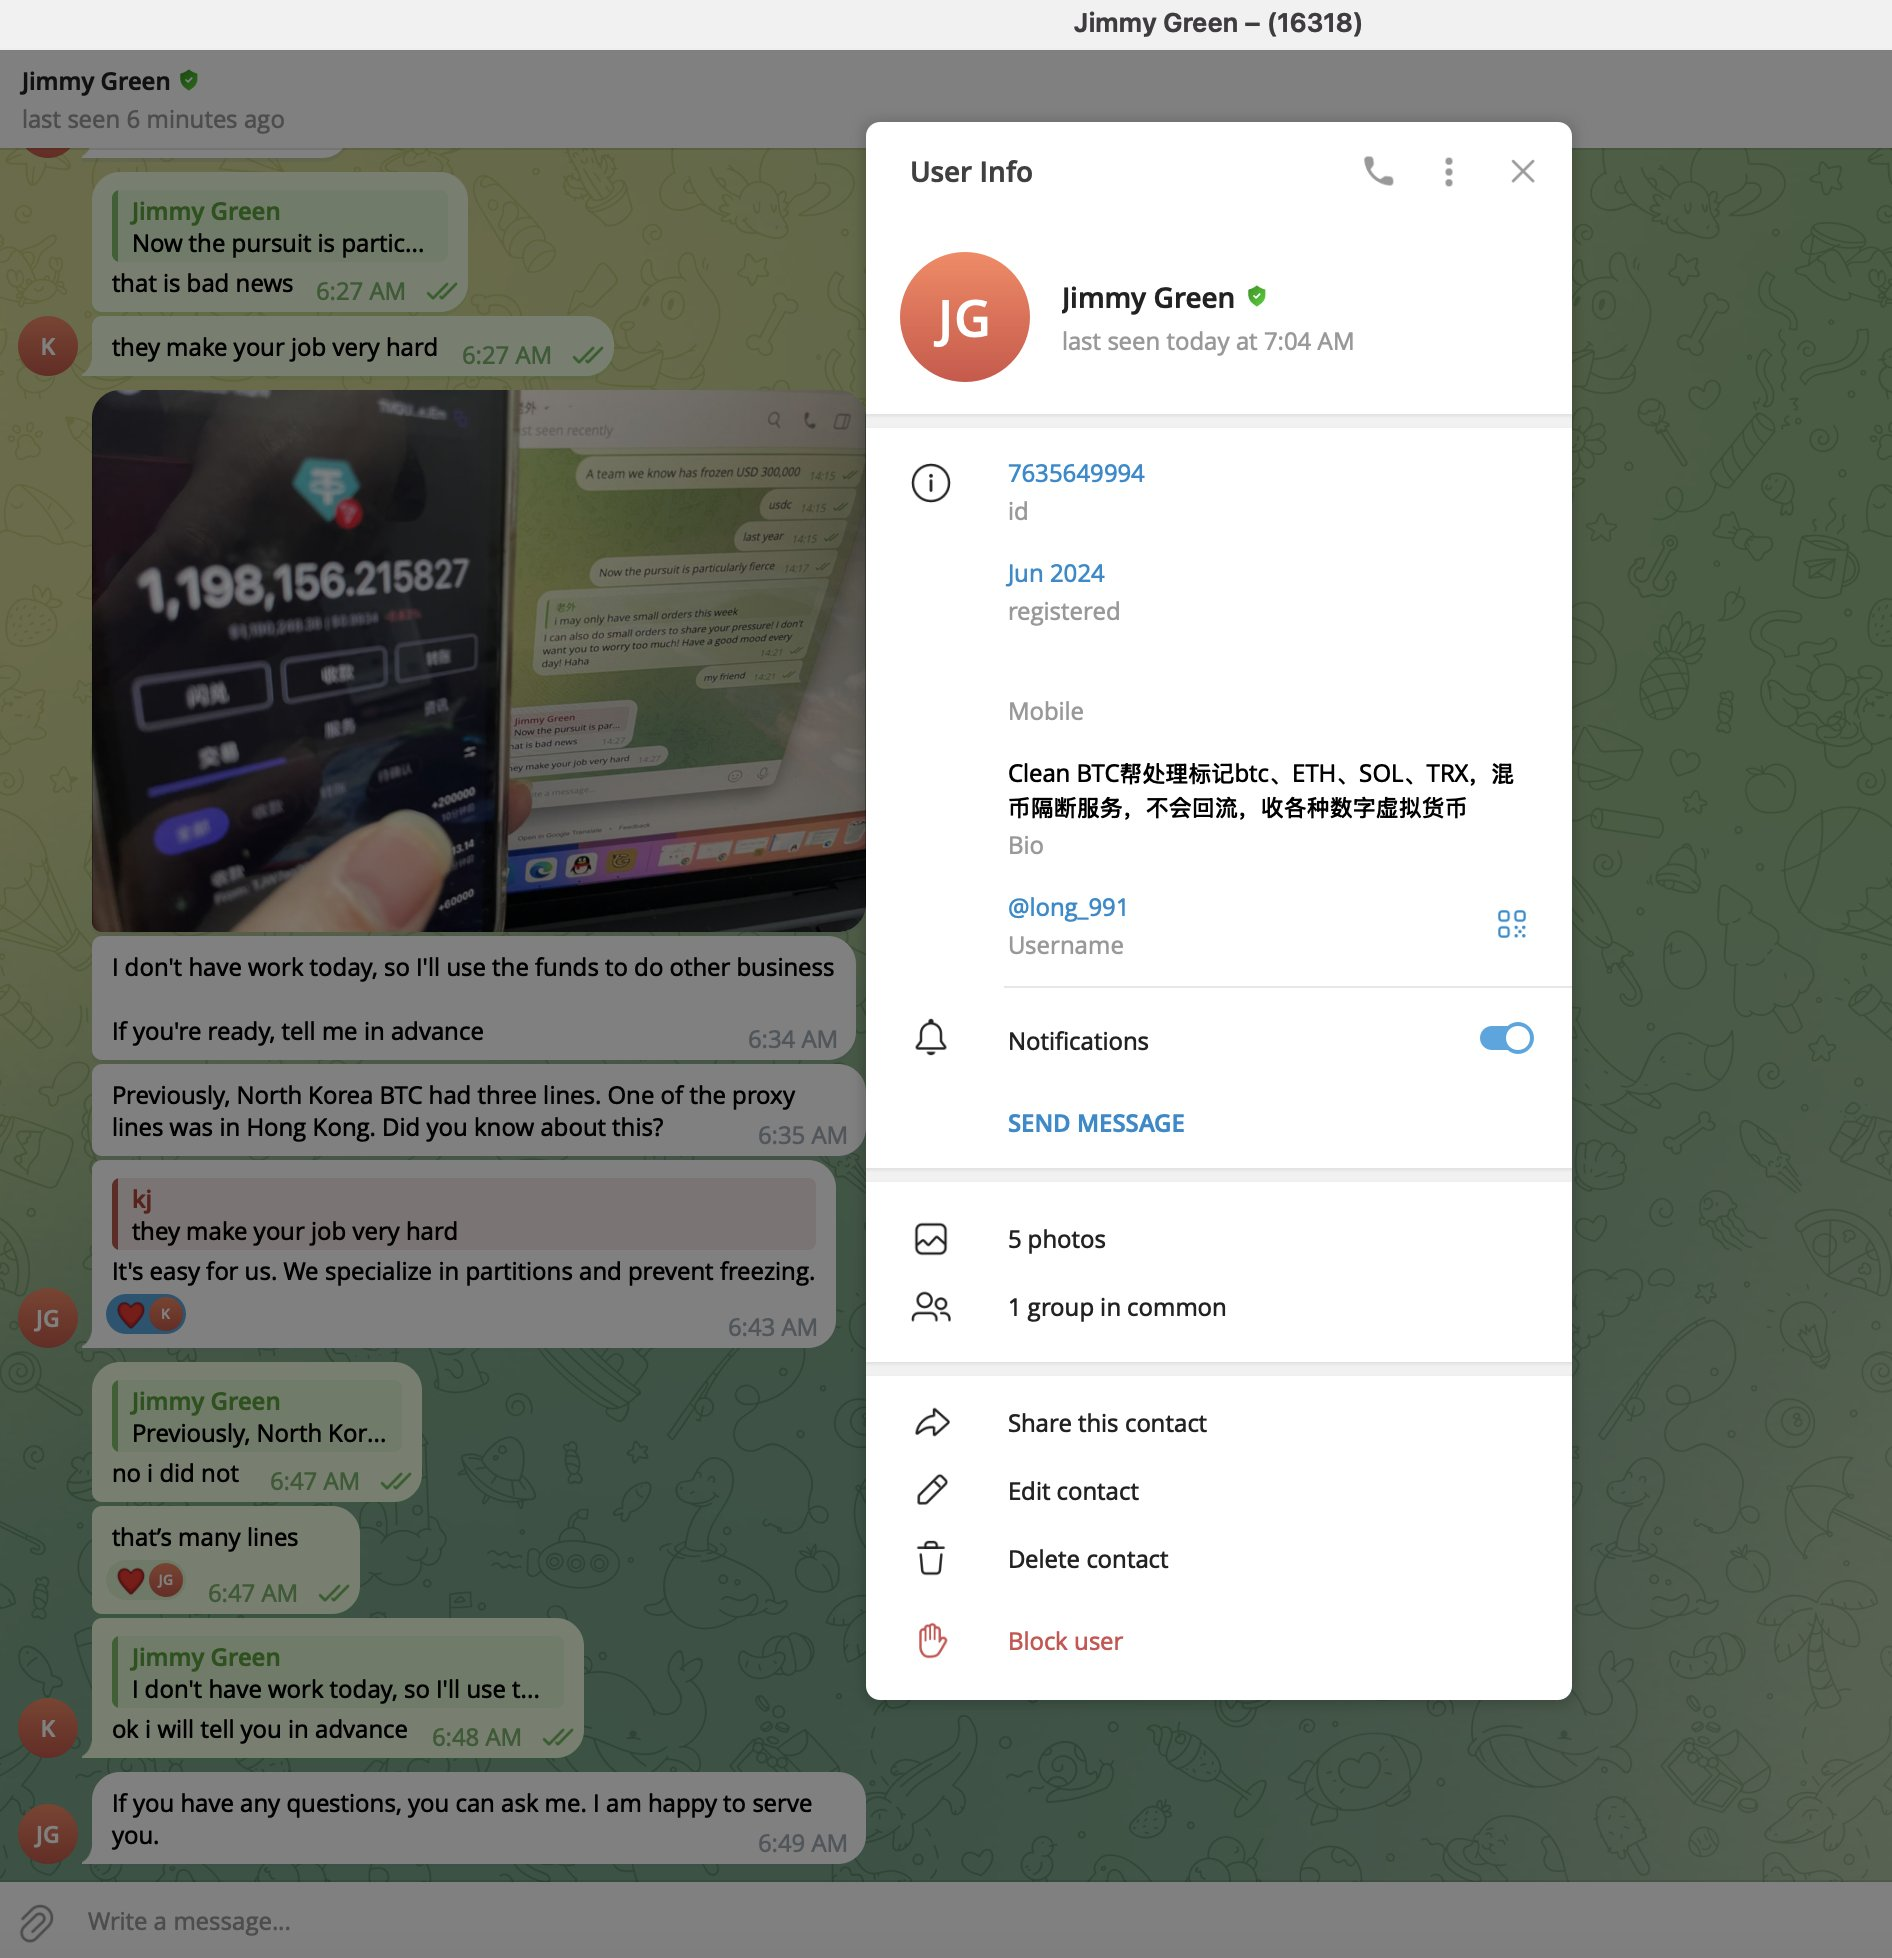
ZachXBT started messaging the accounts that were complaining about orders involving Bybit funds. One of them was called Jimmy Green: Telegram username long_991, ID 7635649994, account registered in June 2024.
Jimmy openly advertises his service in his profile bio. Translated from Chinese, it reads roughly as follows: Clean BTC, we help process marked BTC, ETH, SOL and TRX, coin mixing and link-breaking service, no flowback, we accept all kinds of digital currencies. «No flowback» here is a promise that the money will not return to the sender after a freeze or reversal.
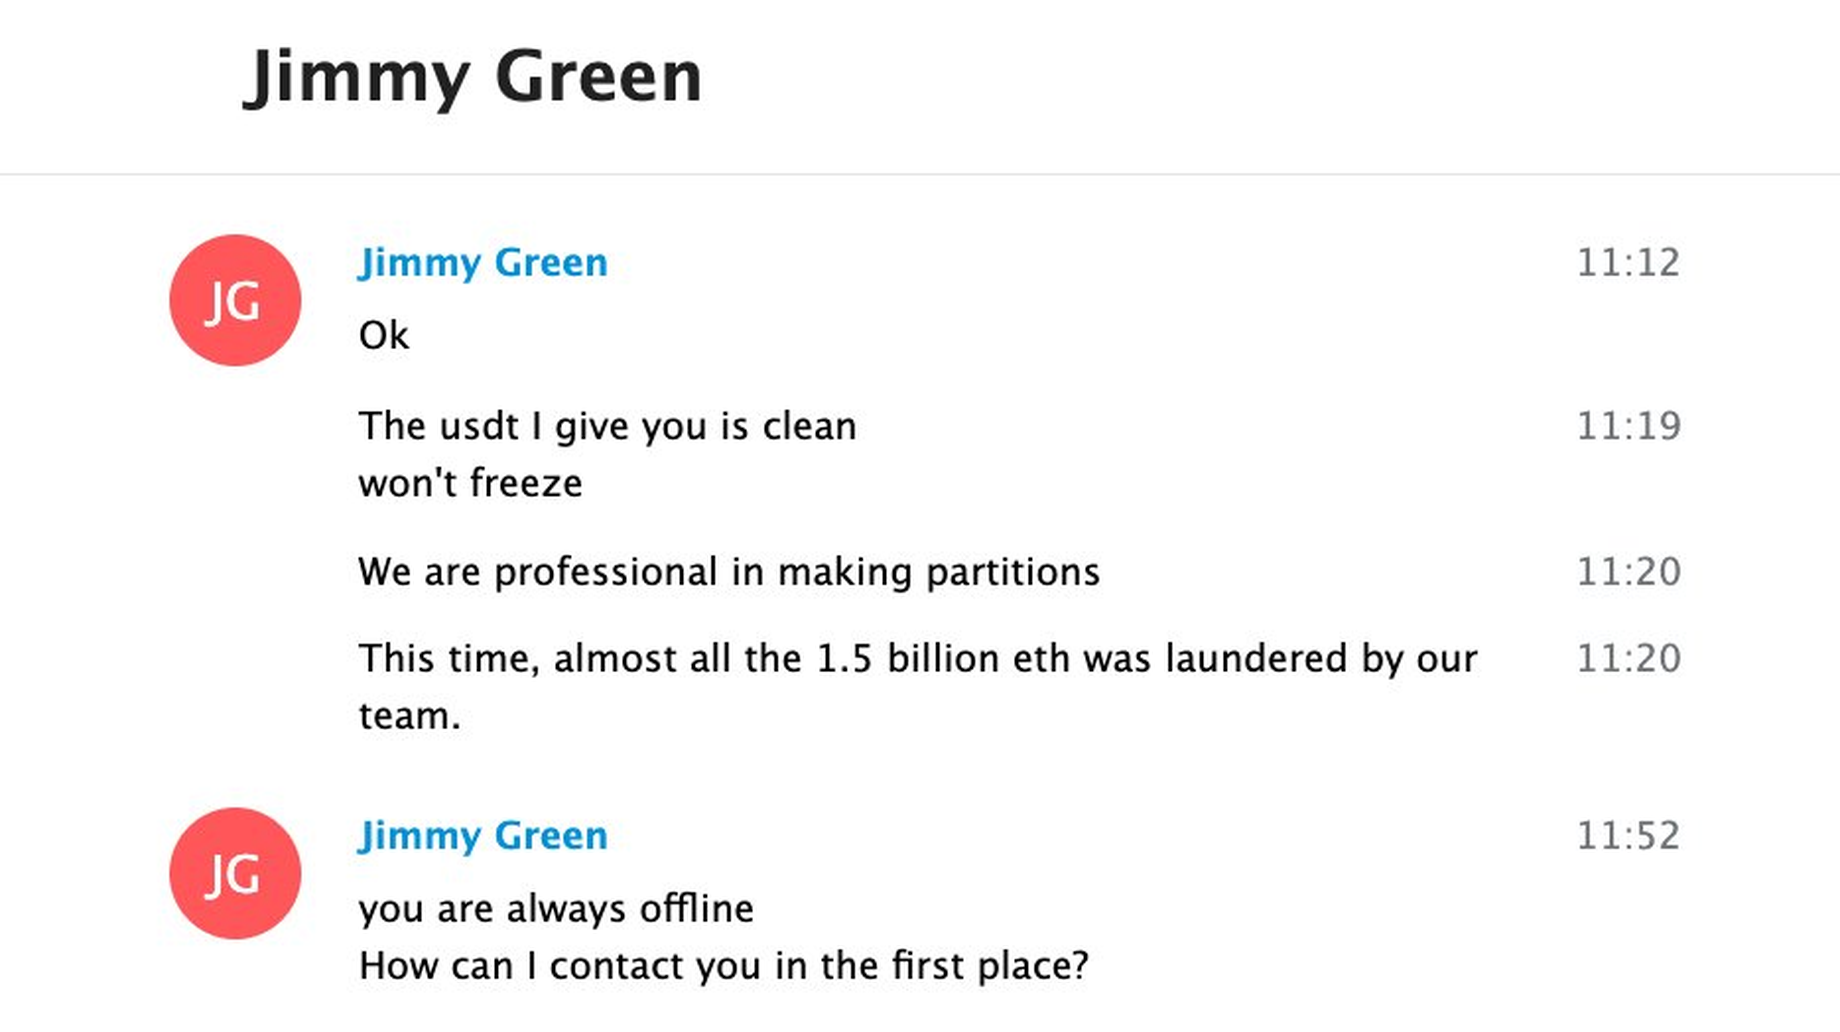
The same chat shows Jimmy sending a photo of a phone with a balance of about 1.2 million USDT, with his own chat in the background with a contact saved as 老外, «foreigner». This, apparently, is what he calls his clients. In the same exchange Jimmy writes that North Korean bitcoin used to have three «lines», one of them running through Hong Kong, and when ZachXBT says how hard their job must be, he replies: «It's easy for us. We specialize in partitions and prevent freezing».
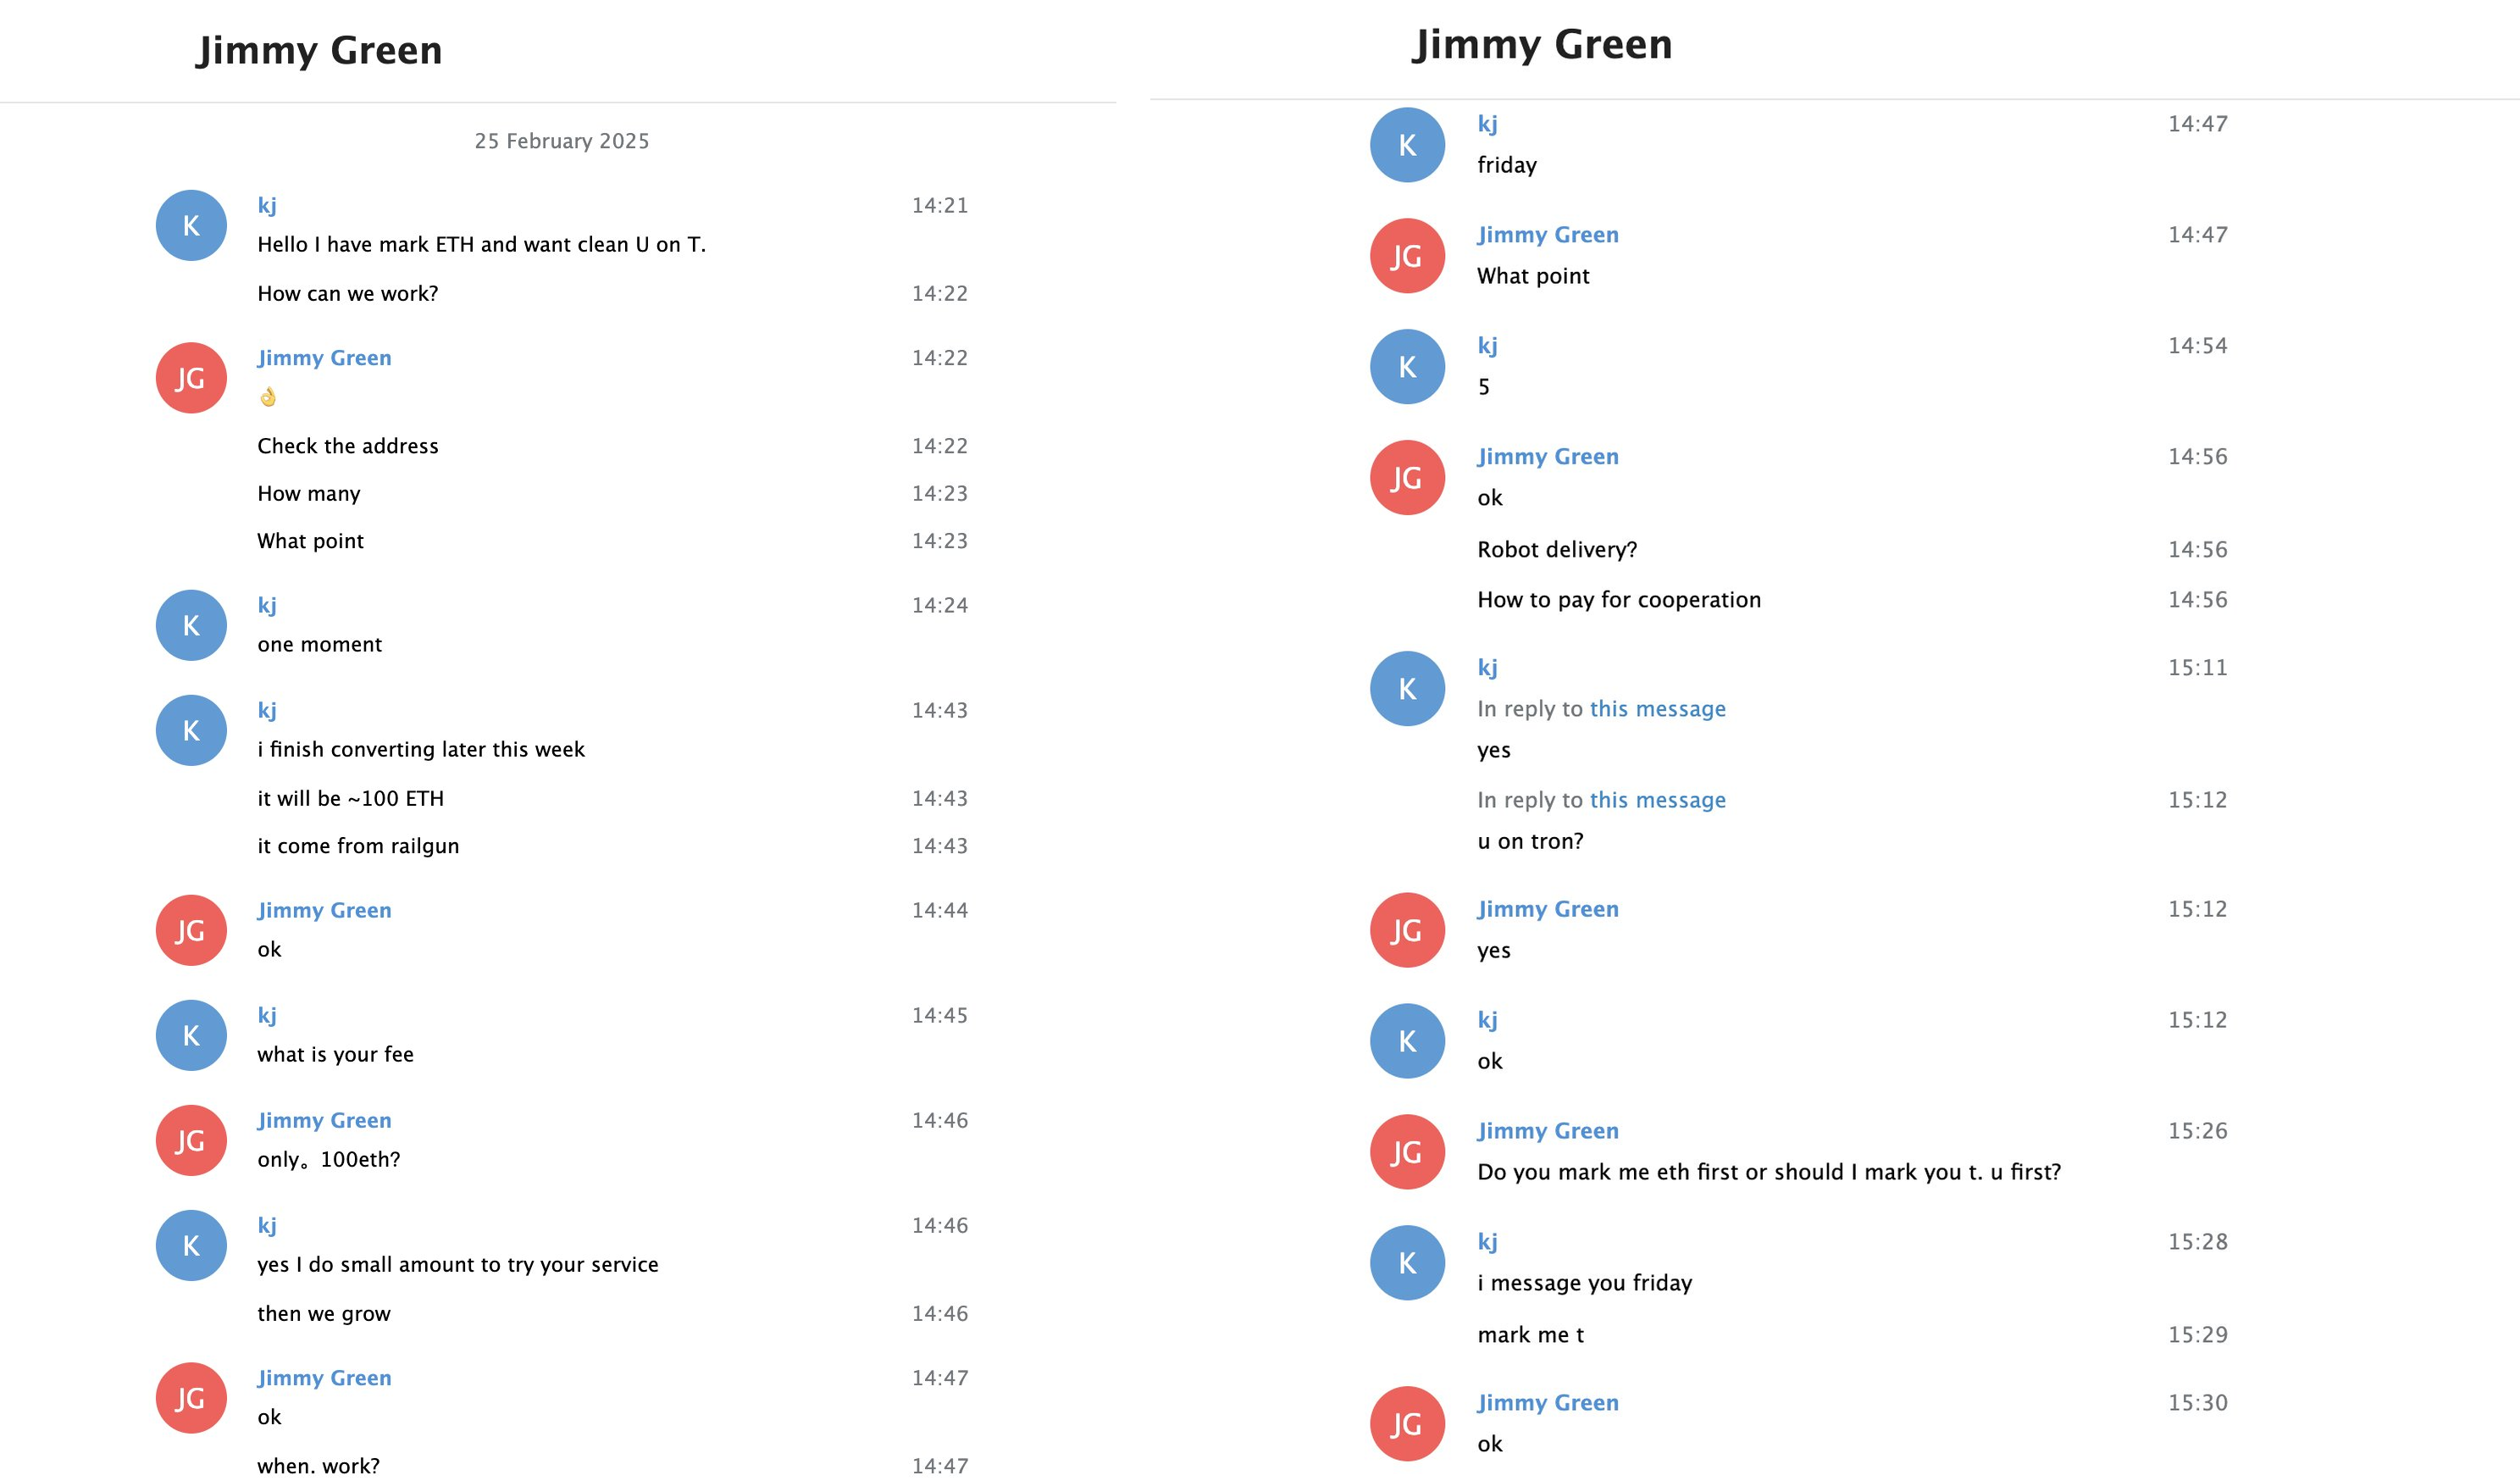
The first conversation took place on February 25, 2025, four days after the hack. ZachXBT introduced himself as a client under the handle kj and wrote that he had marked ETH and wanted clean U on T. Jimmy asked him to check the address and asked about the volume and the fee. ZachXBT replied that he would have about 100 ETH by the end of the week and that the coins came from Railgun, a protocol for private transactions. Jimmy set his terms: work starts from 100 ETH, the fee is 5%, and «robot delivery», an automatic payout, is available.
On the same day, according to ZachXBT's graph, an address from the Bybit cluster sent 64.38 ETH to the wallet 0x7470…b09f, which he labeled as belonging to Jimmy Green, and 4.38 ETH went from there into THORChain. This is the very swap Jimmy was trying to «push through» via support in the THORChain chat.
A $349,700 deal and gas from a Bybit wallet
On March 6, 2025, ZachXBT funded a new Ethereum address with 349,700 USDC, his working capital for trading with Jimmy. He published the address in the thread: 0x073256b50d66a7eb005f2a504d0a4fb6ea62a276.
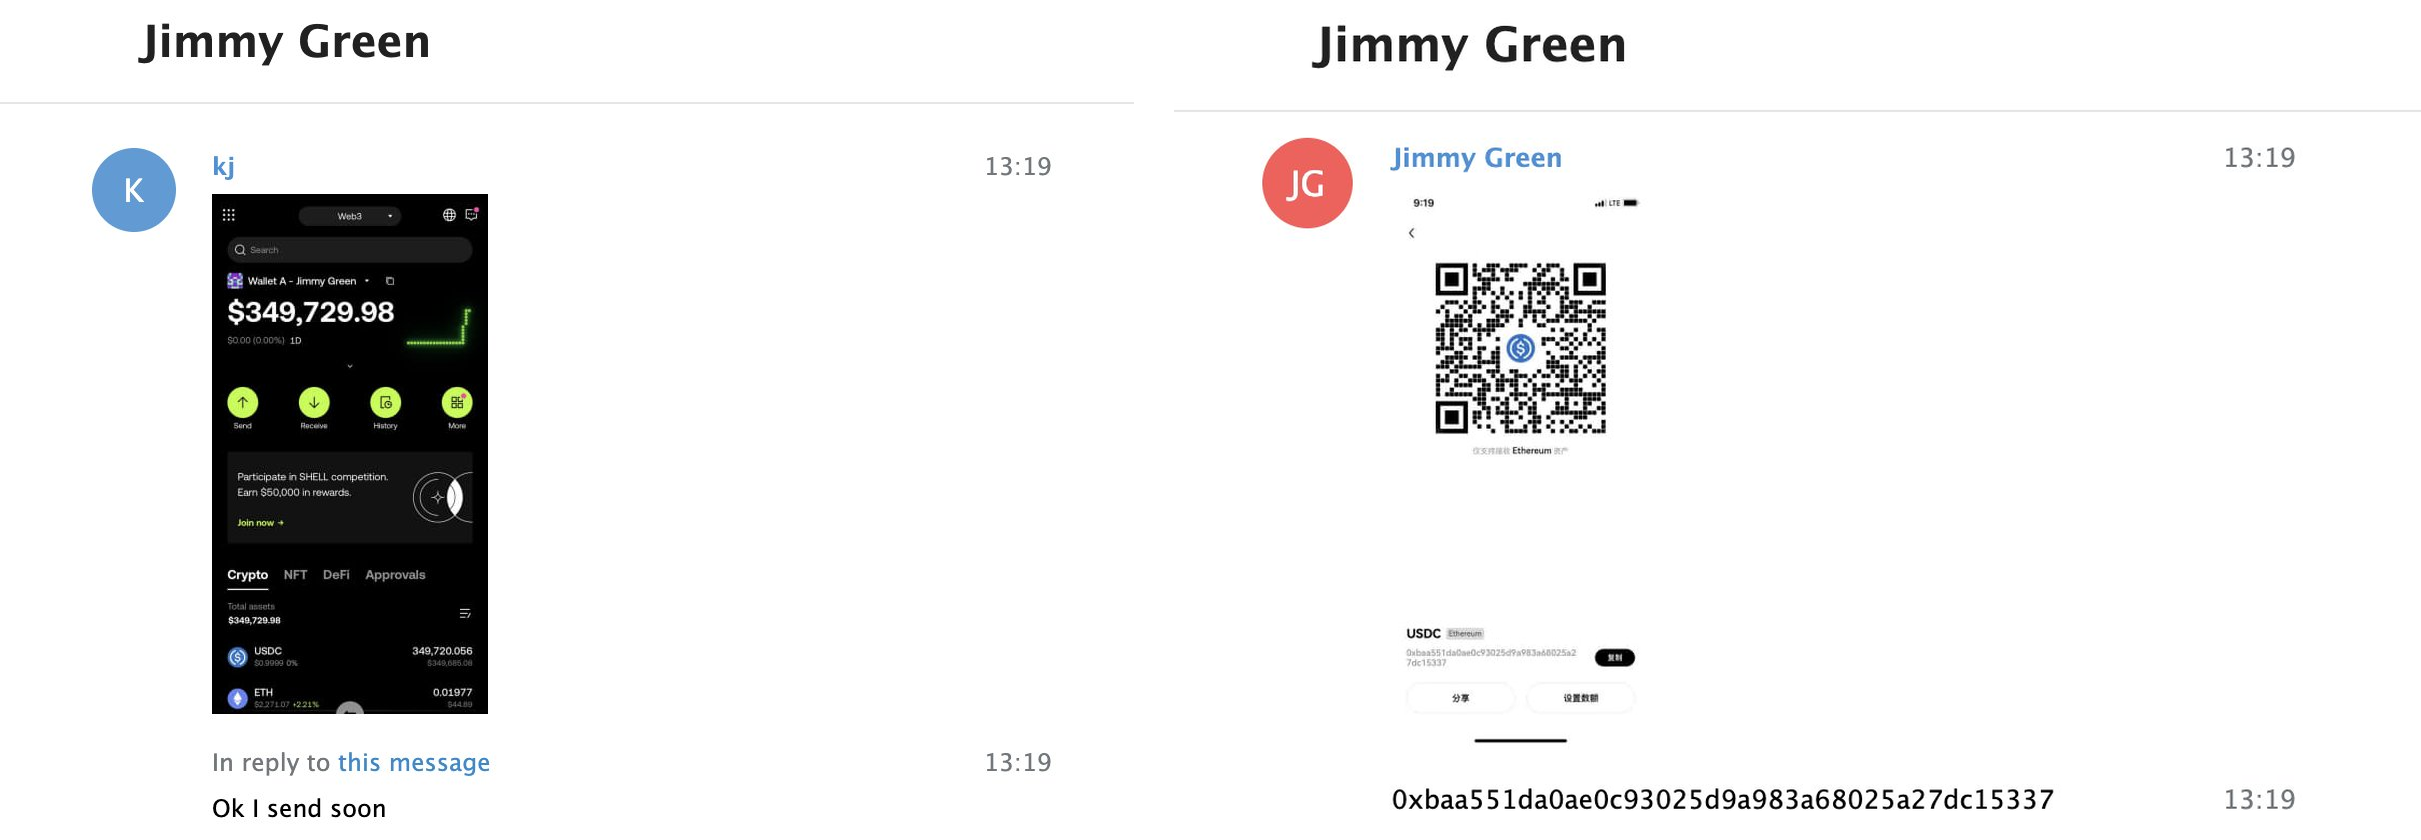
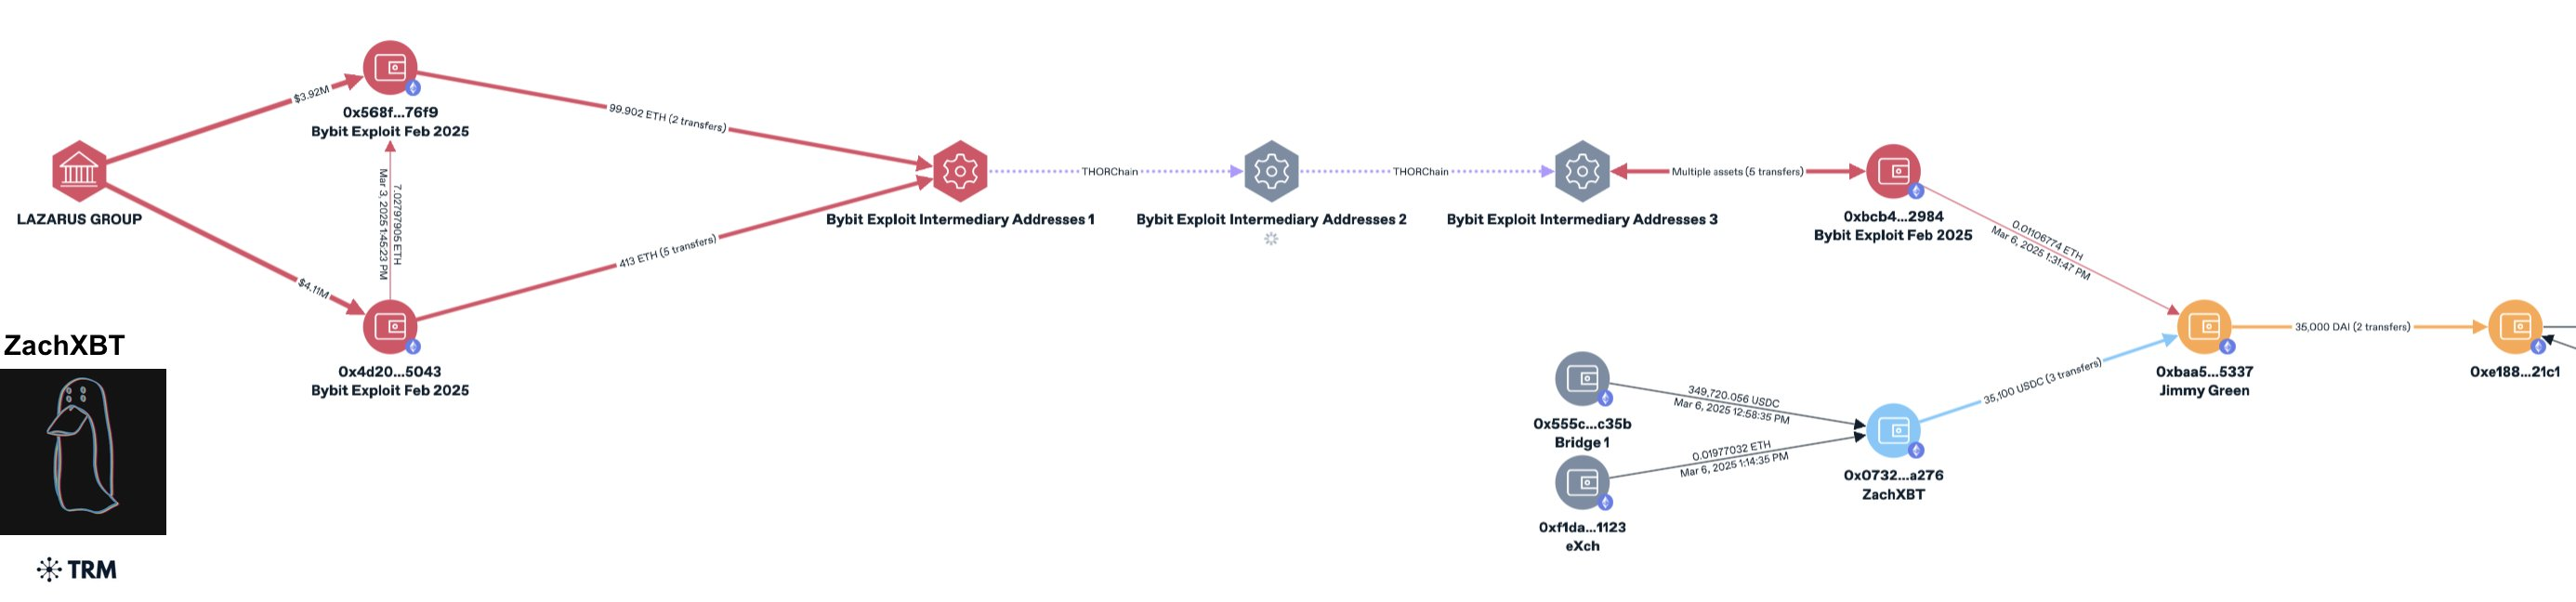
Jimmy provided an address to receive the USDC and was to send USDT on TRON in return. This is where ZachXBT found his first on-chain proof: the gas for Jimmy's address 0xbaa5 came from the wallet 0xbcb4, which is directly traceable to funds from the Bybit hack and is labeled on the public Bybit exploit blacklist site. Put simply, the wallet Jimmy used to receive a client's money was paying its fees with money stolen from Bybit.
The graph also shows ZachXBT's own funds moving: 35,100 USDC went to Jimmy's address in three transfers, and Jimmy sent 35,000 DAI onward.
Jimmy Green addresses published by ZachXBT:
To build trust, ZachXBT completed several more trades with Jimmy. The launderer was cautious too. In one message he writes:
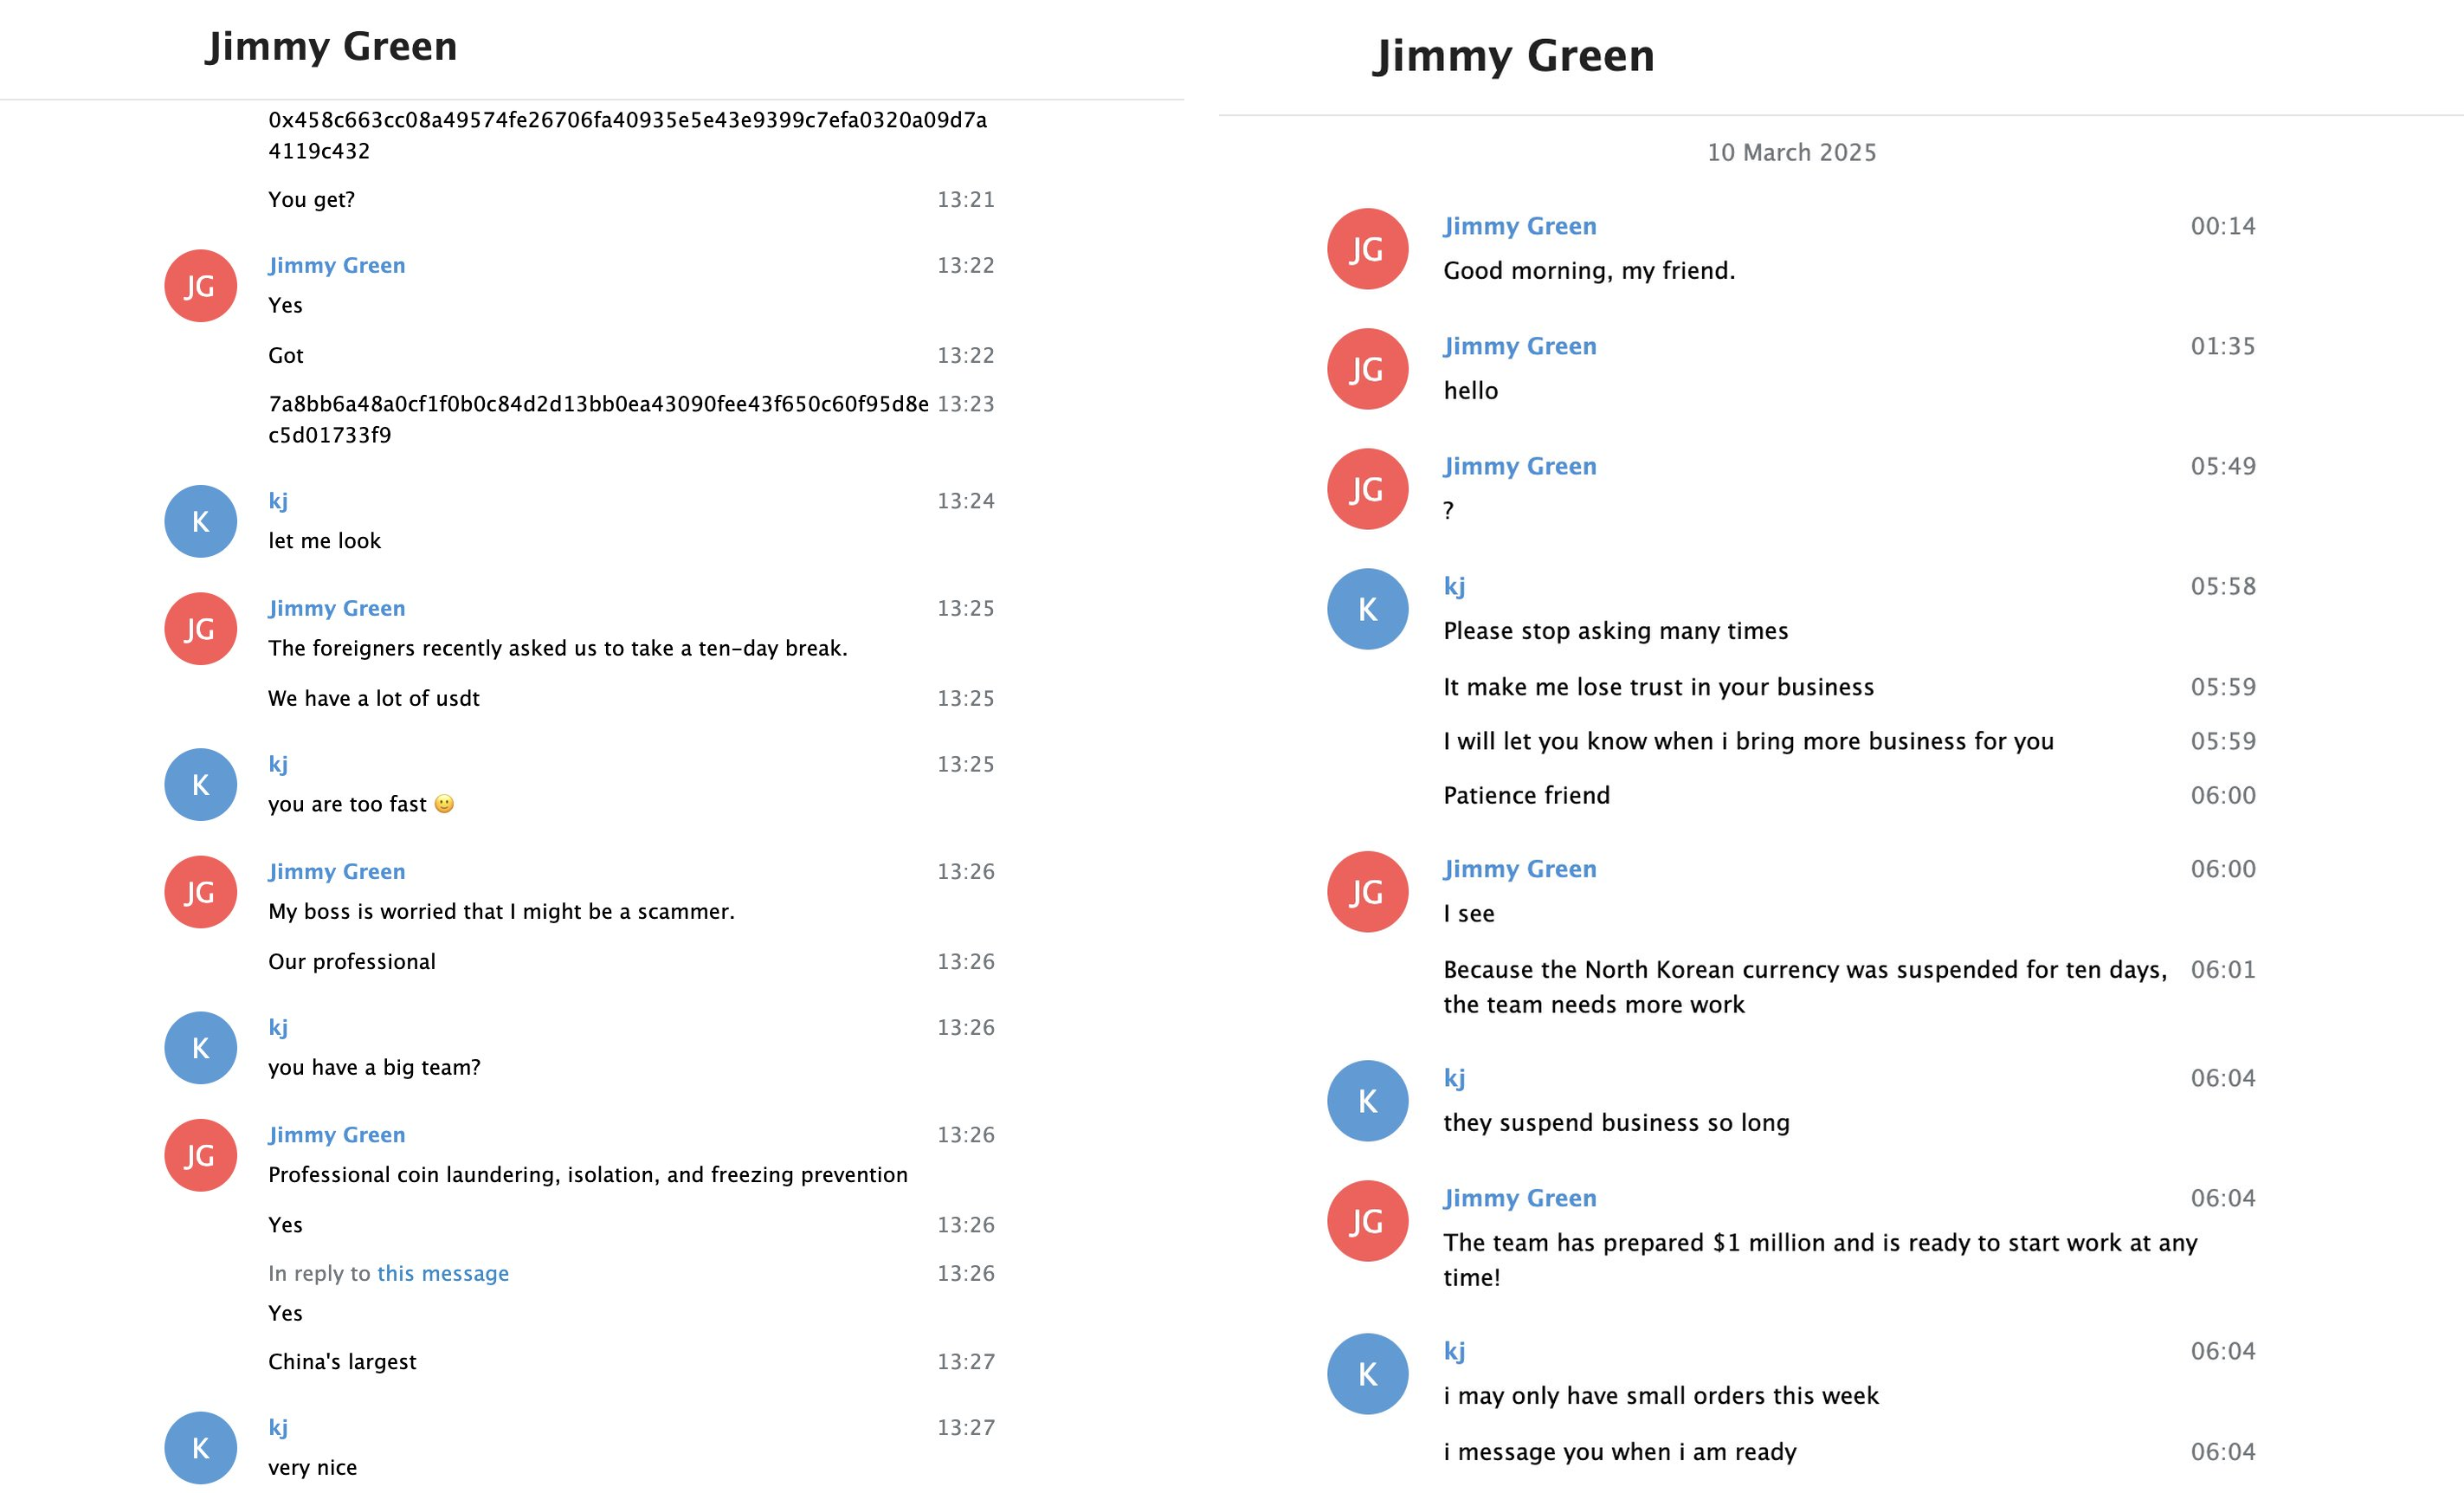
My boss is worried that I might be a scammer, – Jimmy Green wrote in the chat published by ZachXBT.
Asked whether he had a big team, Jimmy replied that he does «professional coin laundering, isolation, and freezing prevention» and called his group the largest in China.
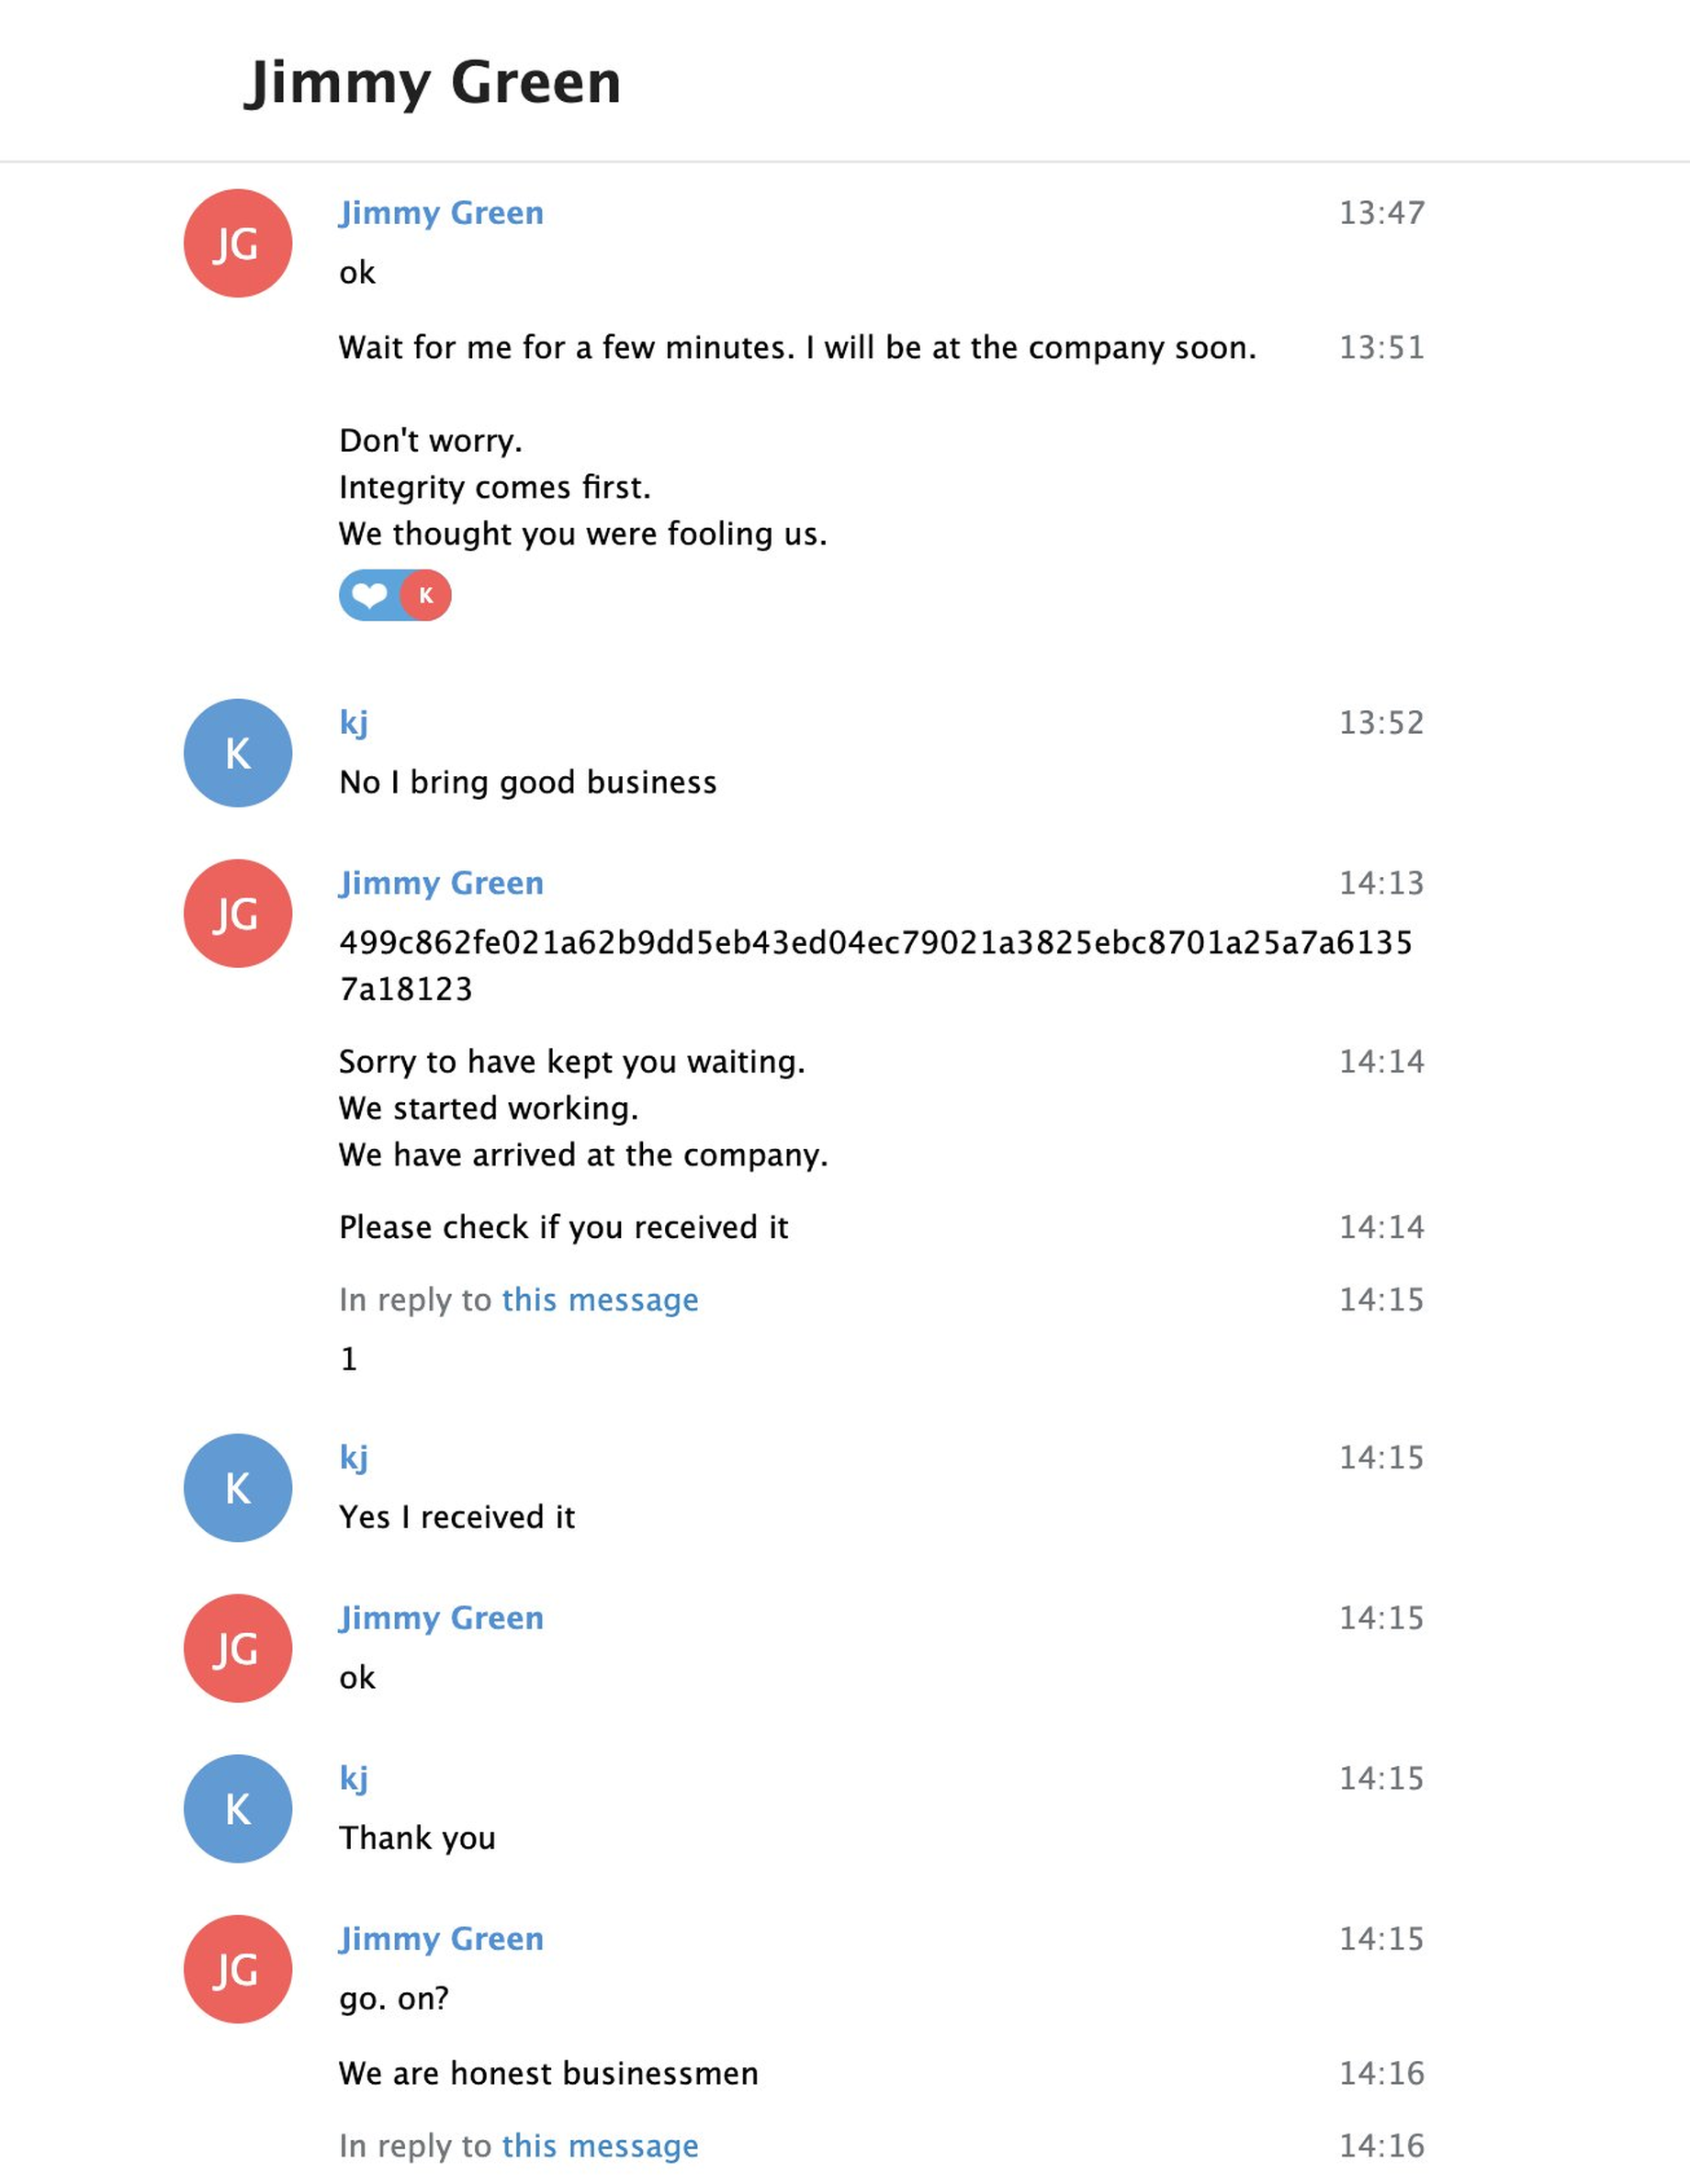
On March 10, Jimmy was pressing ZachXBT for new trades: «the North Korean currency» had been suspended for ten days, the team needed work and had already prepared $1 million.
After one of the trades, Jimmy admitted that his team had suspected ZachXBT of trying to fool them, and immediately reassured him: «Integrity comes first», «We are honest businessmen».
What Jimmy revealed about his work
Once trust was established, Jimmy began to speak more openly. The chats add up to a fairly detailed picture of how such a service works.
The client is North Korea, and no one hides it. Jimmy calls his clients either «foreigners» or simply North Korea. In one message he explains a pause in work by saying the «foreigners» asked them to take a ten-day break; in another, that «the North Korean currency» was suspended for ten days. In the chats, Jimmy and ZachXBT regularly joke about Kim Jong-un: «Kim Jong-un called for a halt to the work. The coins they sent back were too dirty. They are being investigated». In another message, Jimmy writes that he is washing bitcoins from North Korea that day and that Kim Jong-un «only released» 50 BTC, of which his team received 30. If he is to be believed, the same flow of North Korean money is shared among several groups, which matches his story about the three «lines».
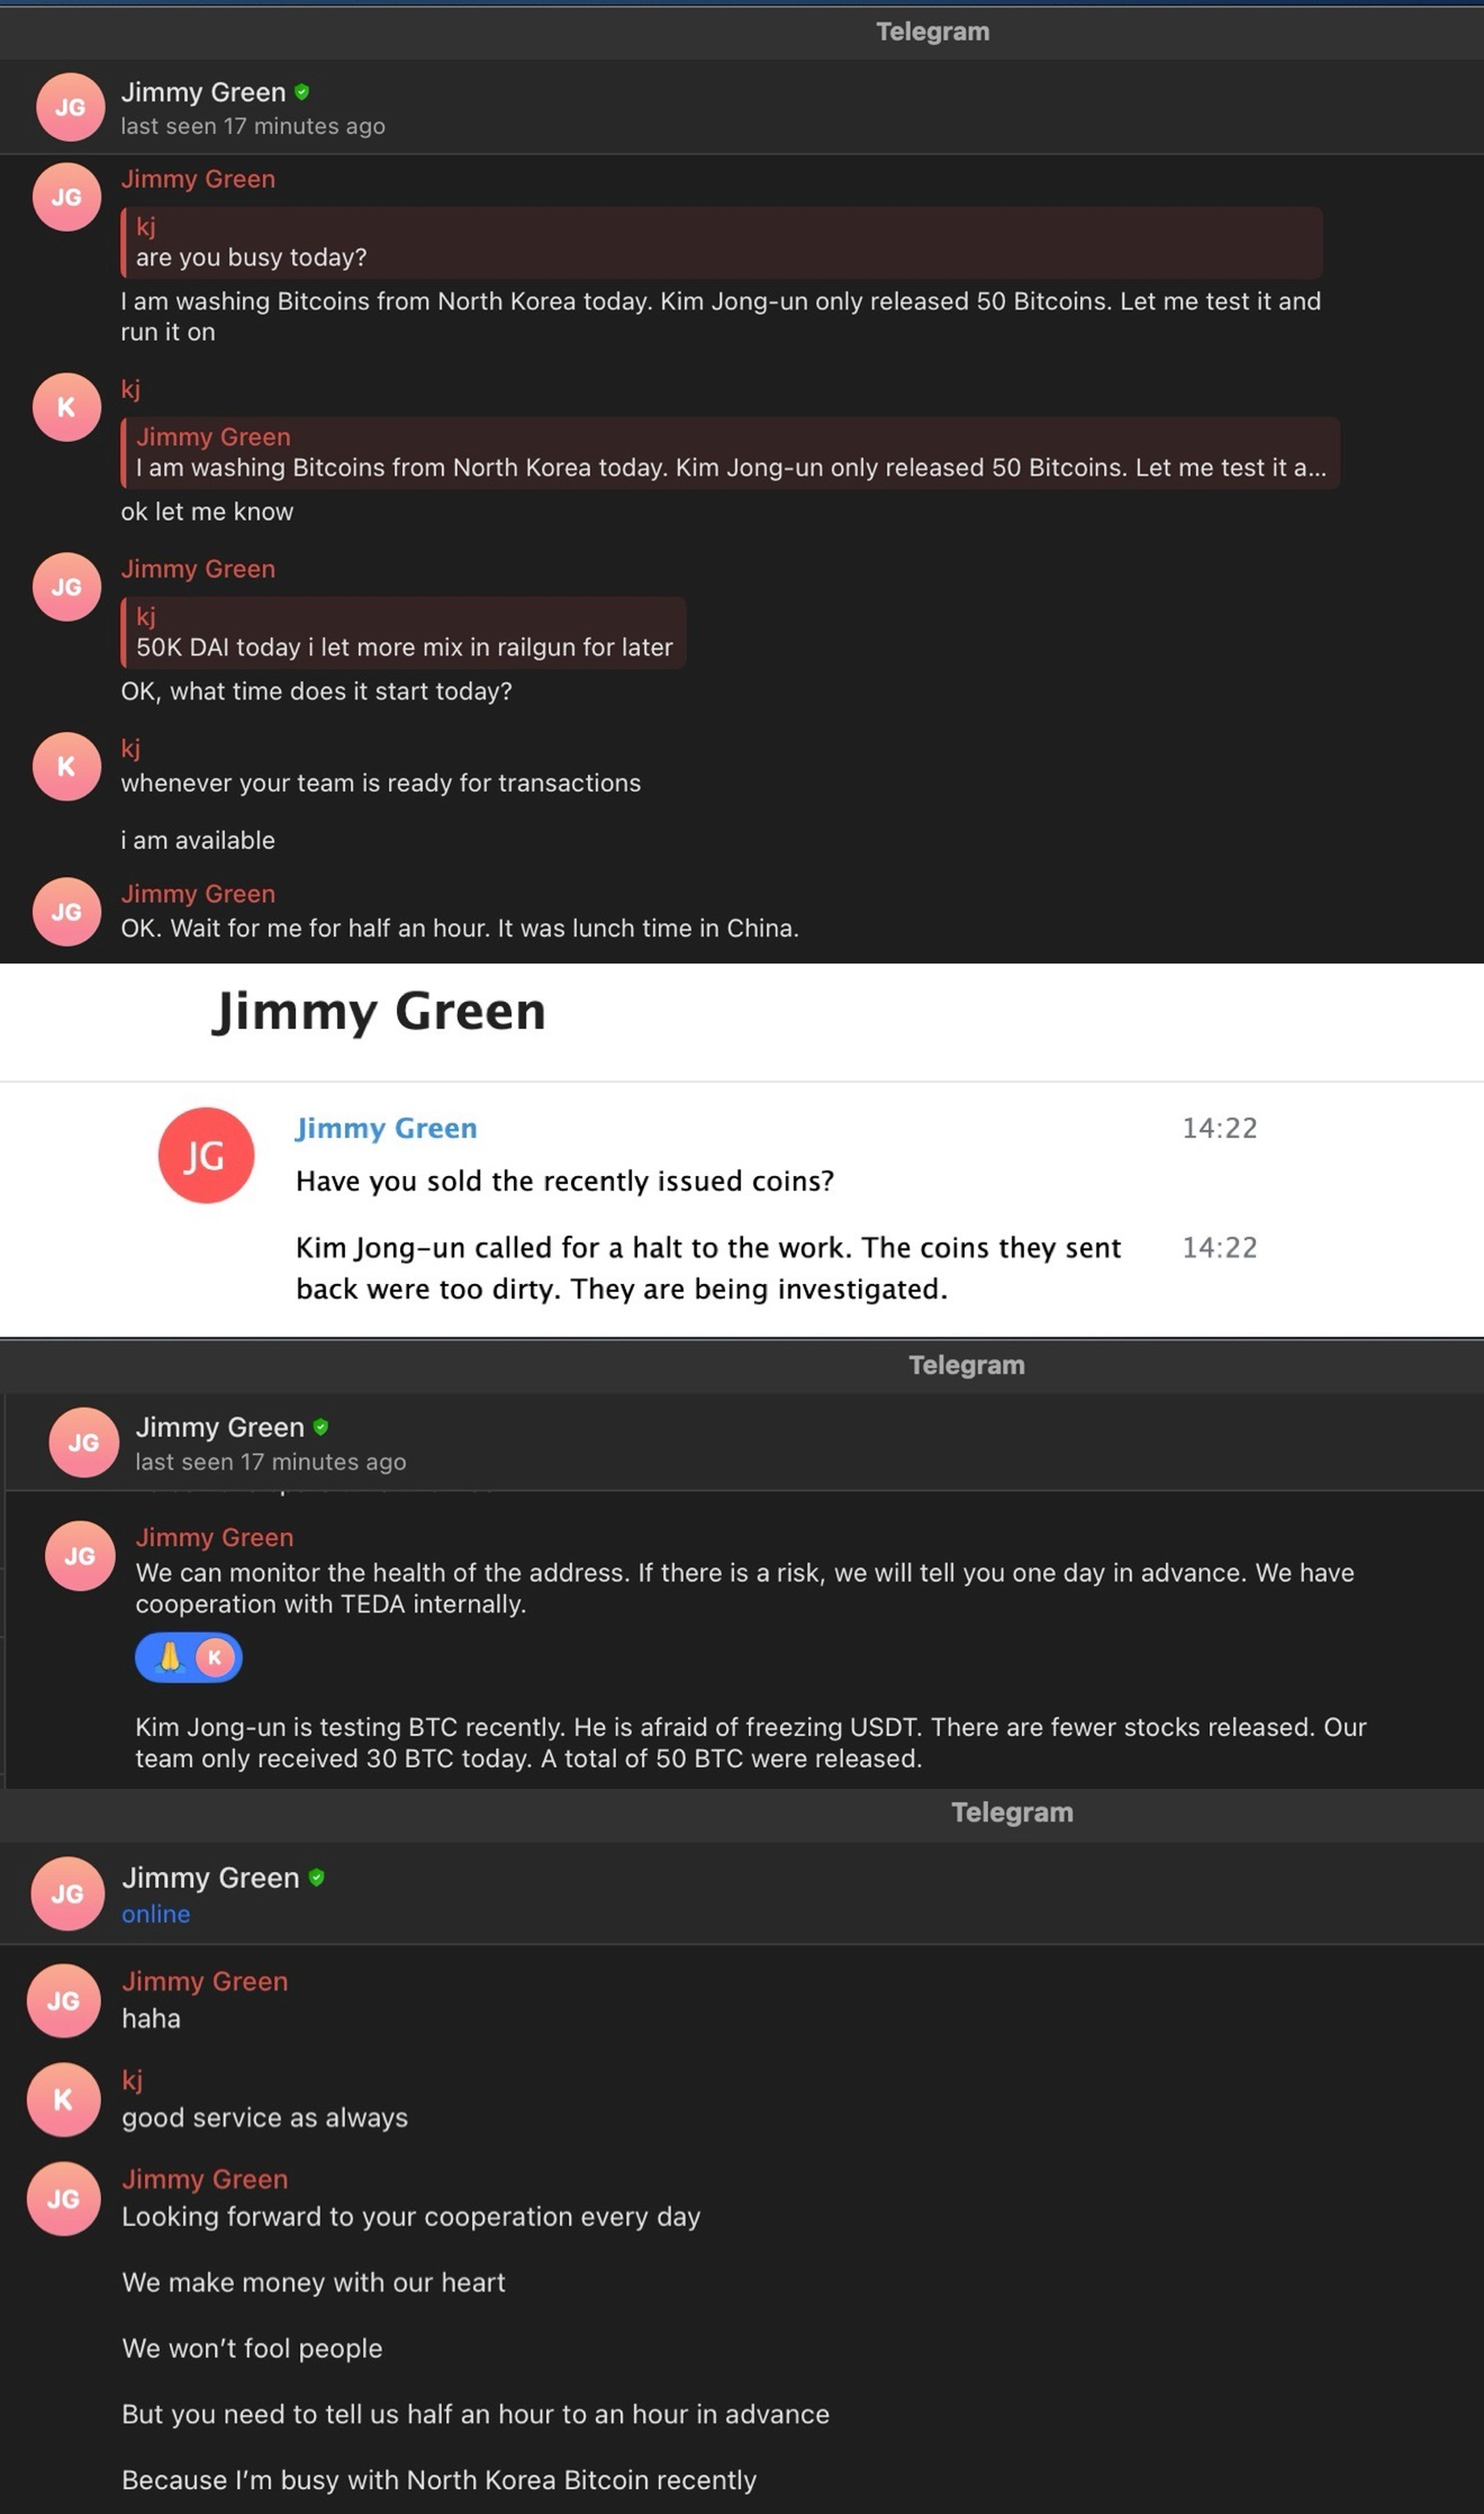
Freeze protection as the main product. Jimmy claimed his team monitors the «health» of addresses and will warn a client a day in advance if a risk appears. In the same message he claimed «cooperation with TEDA internally». This most likely refers to Tether: in Chinese crypto slang, USDT is called 泰达币, «Taida coin». There is no confirmation of this, and it should be treated as advertising for the service rather than fact. But the wording itself shows what the clients of such services fear most: having their USDT frozen by the issuer.
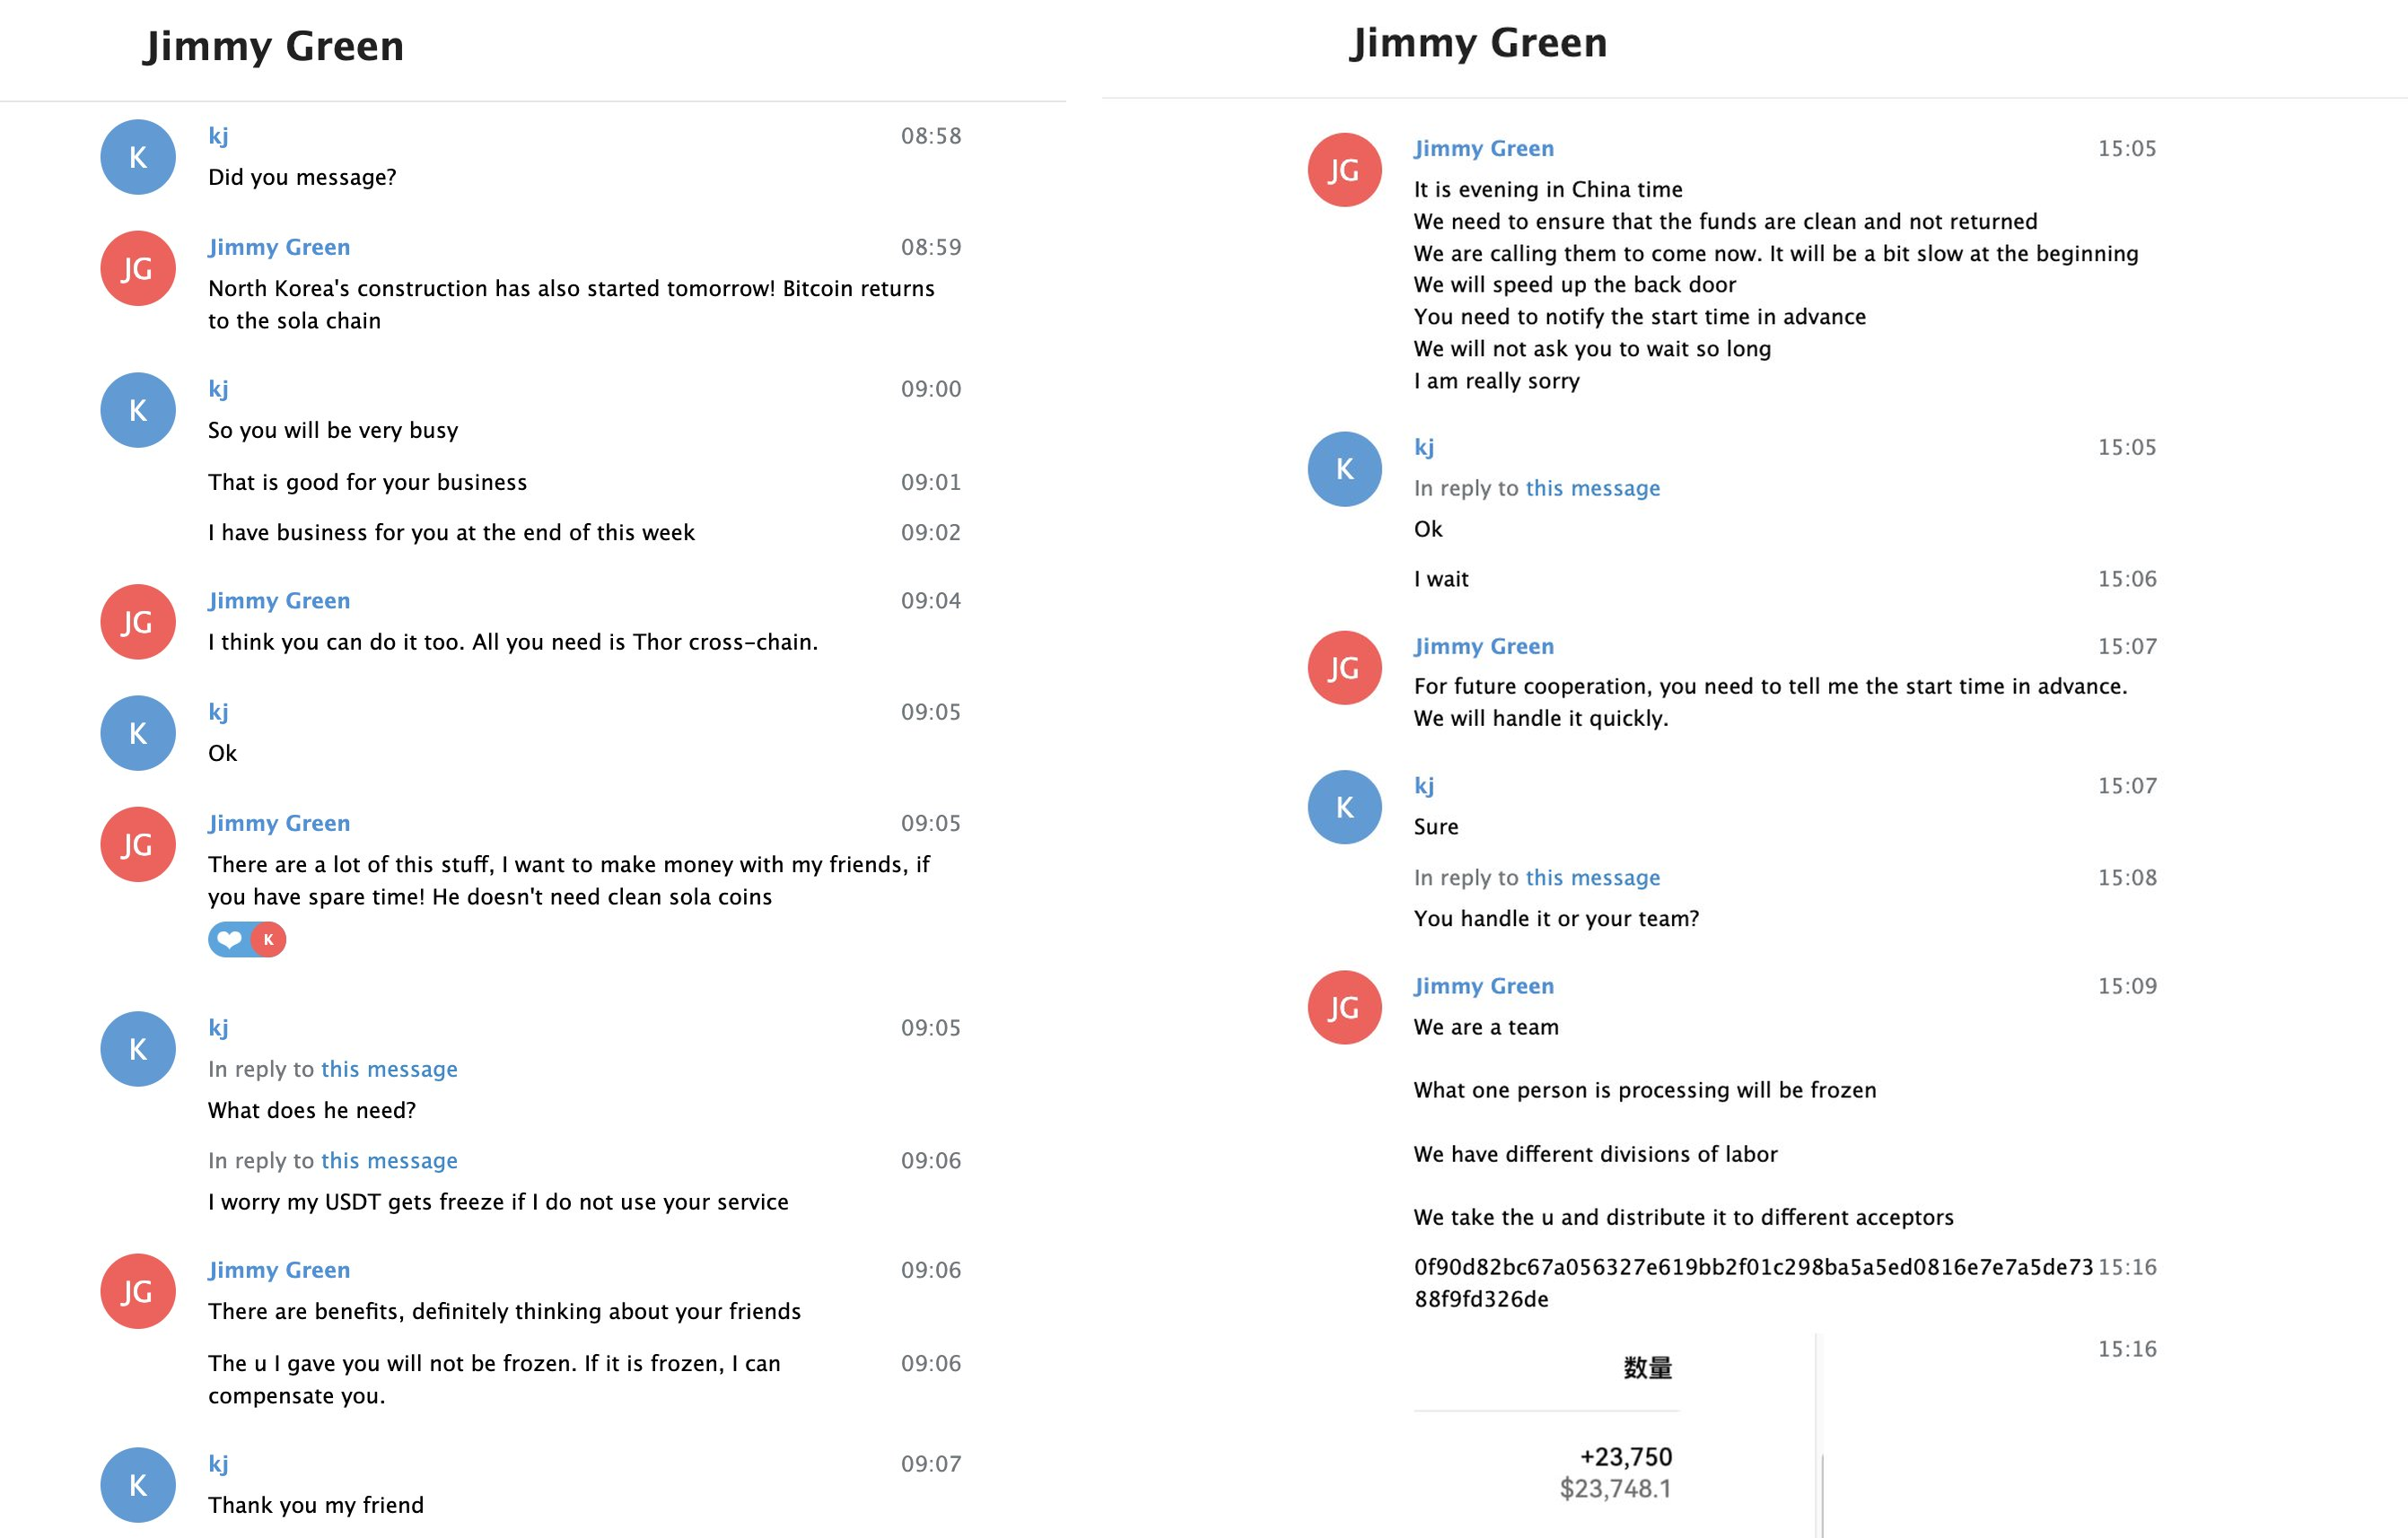
A guarantee in case of a freeze. When ZachXBT wrote that he was worried about his USDT being frozen, Jimmy promised that the coins he provided would not be frozen, and that if they were, he would compensate the loss.
Division of labor. Jimmy described the group as a team where everyone has their own role. According to him, if the funds one person is processing get frozen, the rest of the chain keeps working. He also wrote that the team takes the USDT and distributes it among different «acceptors». In the same exchange he warns that the next day «North Korea's construction» starts and the bitcoin will go to Solana, and suggests that ZachXBT take up this work himself: «All you need is Thor cross-chain».
This last point matters not only for investigators. Acceptors sell USDT on the over-the-counter market and on P2P, so coins with this origin sooner or later end up with ordinary sellers and buyers.
Where dirty crypto comes from and how it reaches ordinary people22 Eyl 2026Devamını oku
How ZachXBT checked Jimmy's words on-chain
The real value of the thread is not the chats themselves but the fact that most of what Jimmy said could be checked against on-chain data.
A predicted route. Once, Jimmy wrote that the funds would go to Solana the next day. The next day, they did. Jimmy also said that his team had laundered most of the $1.5 billion from Bybit. ZachXBT writes that this is consistent with the patterns he observed, but he did not quantify that share himself.
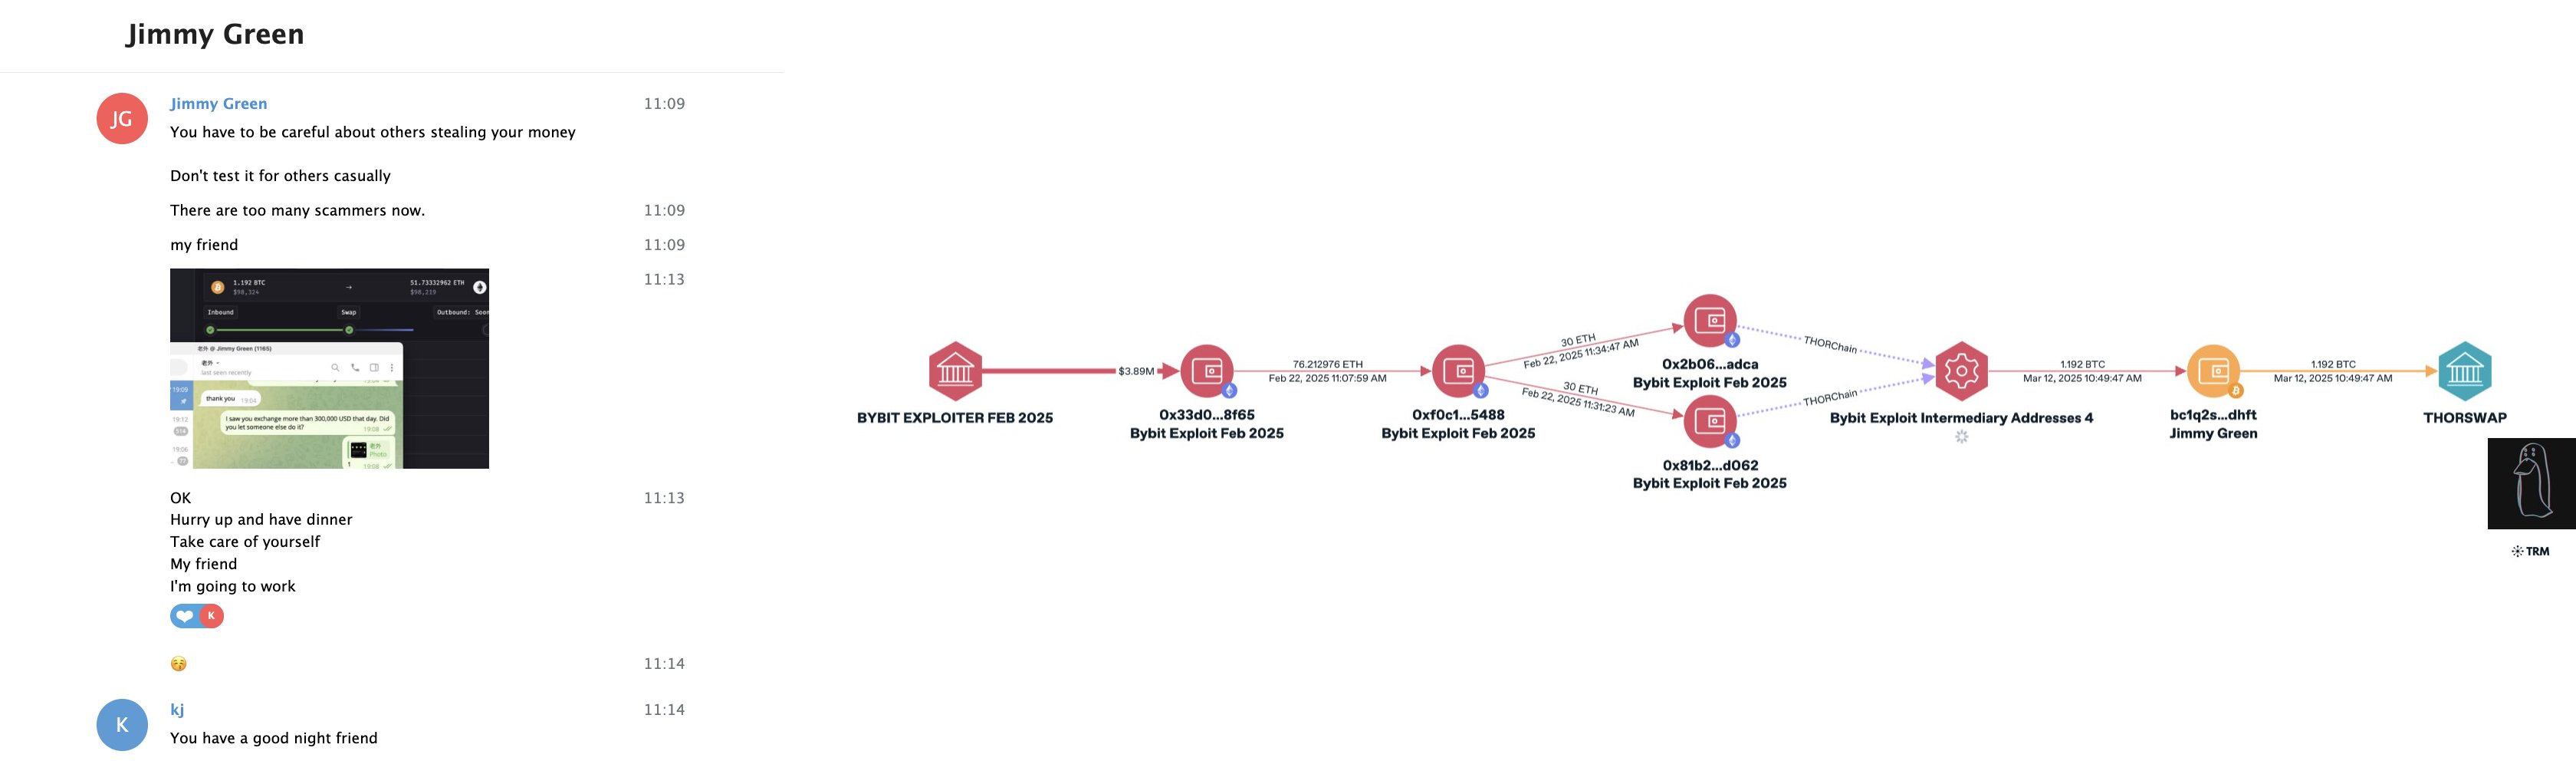
A screenshot that matched THORChain. On March 12, 2025, Jimmy sent a screenshot of himself bridging funds. ZachXBT matched the amounts and timing against the THORChain explorer and found an order created within minutes of the message. On his graph the path looks like this: the Bybit exploiter's address → several intermediate Bybit Exploit addresses → the bitcoin address bc1q2s…dhft, labeled as Jimmy Green → THORSwap. Transaction hash: 81a85130b36057428e64b6f97215f77b5a197776a8f1b3a61c8cd0ee1ebfa8c1.
The image Jimmy sent shows a swap of 1.192 BTC for 51.73 ETH, and the graph shows the same 1.192 BTC arriving at Jimmy's address from Bybit funds and leaving for THORSwap on March 12 at 10:49.
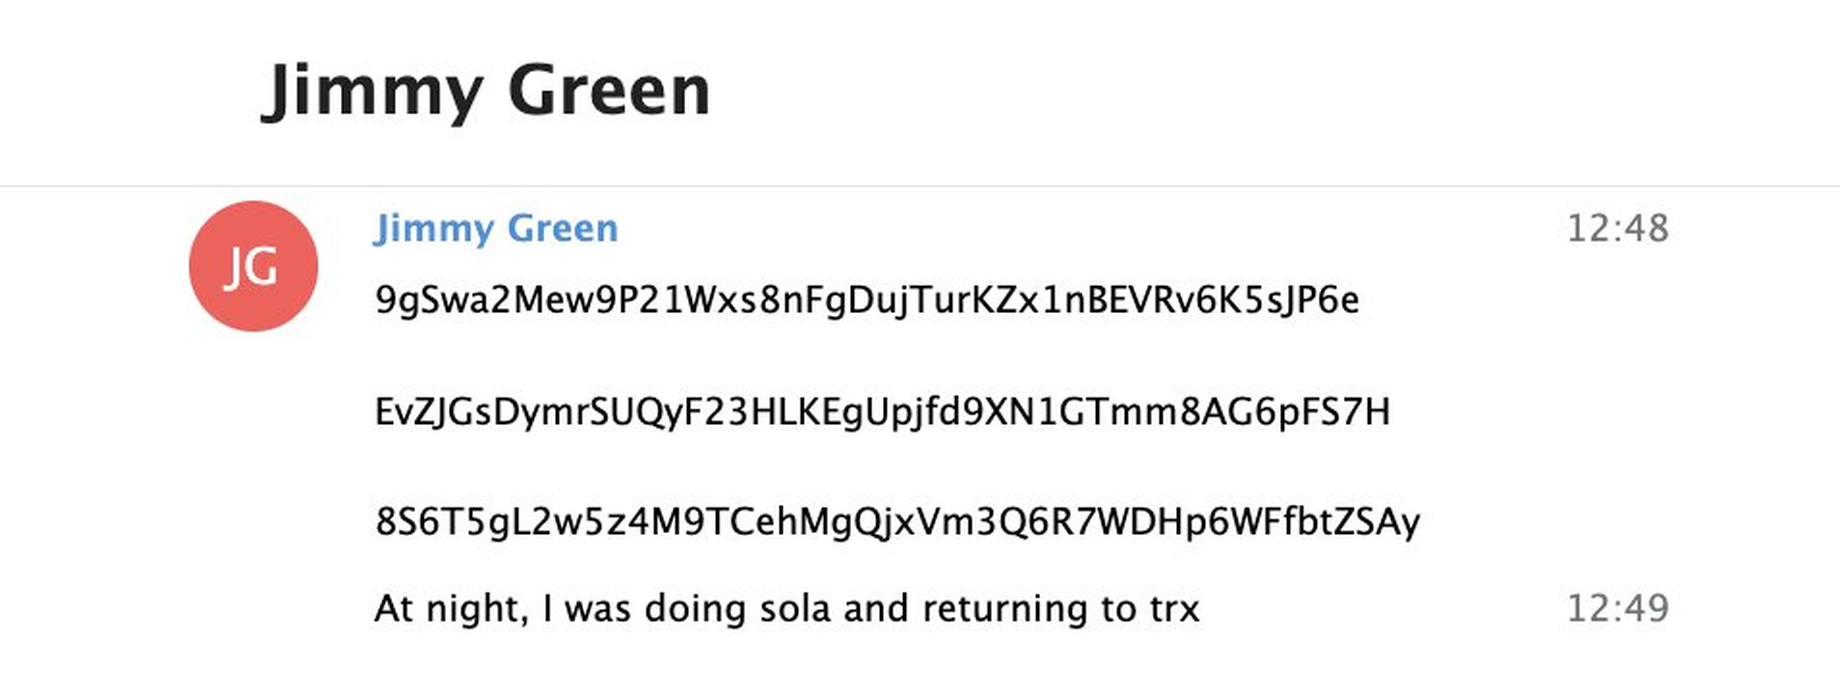
A $12 million cluster and a Tether freeze. Jimmy shared three Solana addresses and added: «At night, I was doing sola and returning to trx».
These addresses led ZachXBT to a cluster of wallets through which more than $12 million in Bybit funds was being swapped in real time along the route BTC → ETH → SOL → TRON. Tether later froze 442,000 USDT linked to this cluster at the address 0x652d7f9edaaa8891be2de74ea568d70af823d89e. ZachXBT's graph shows a different figure next to this freeze, 456,000 USDT in March 2025, while the text of the thread says 442,000.
A new method: laundering through liquidity pools with illiquid tokens
In the same cluster, ZachXBT spotted a method he calls new: laundering through Uniswap liquidity pools using illiquid tokens. In the thread he describes it in a single sentence, but the cluster graph shows what it looked like.
First, the Bybit funds went through the Tornado Cash mixer. The money then entered about a dozen pools where little-known tokens with names like FIZZ, BUTTER, ZIPPY, SQUEE or GOLLUM traded against USDT. For one of the tokens, the graph also marks the address that created it. From the pools, USDT spread out across exchange deposit addresses – the graph shows OKX, BigONE, Gate, CoinEx and HTX – and the funds then moved to Solana, went through a swap in Bitget Wallet and were consolidated on TRON addresses. A Tether freeze is also marked next to one of the pools.
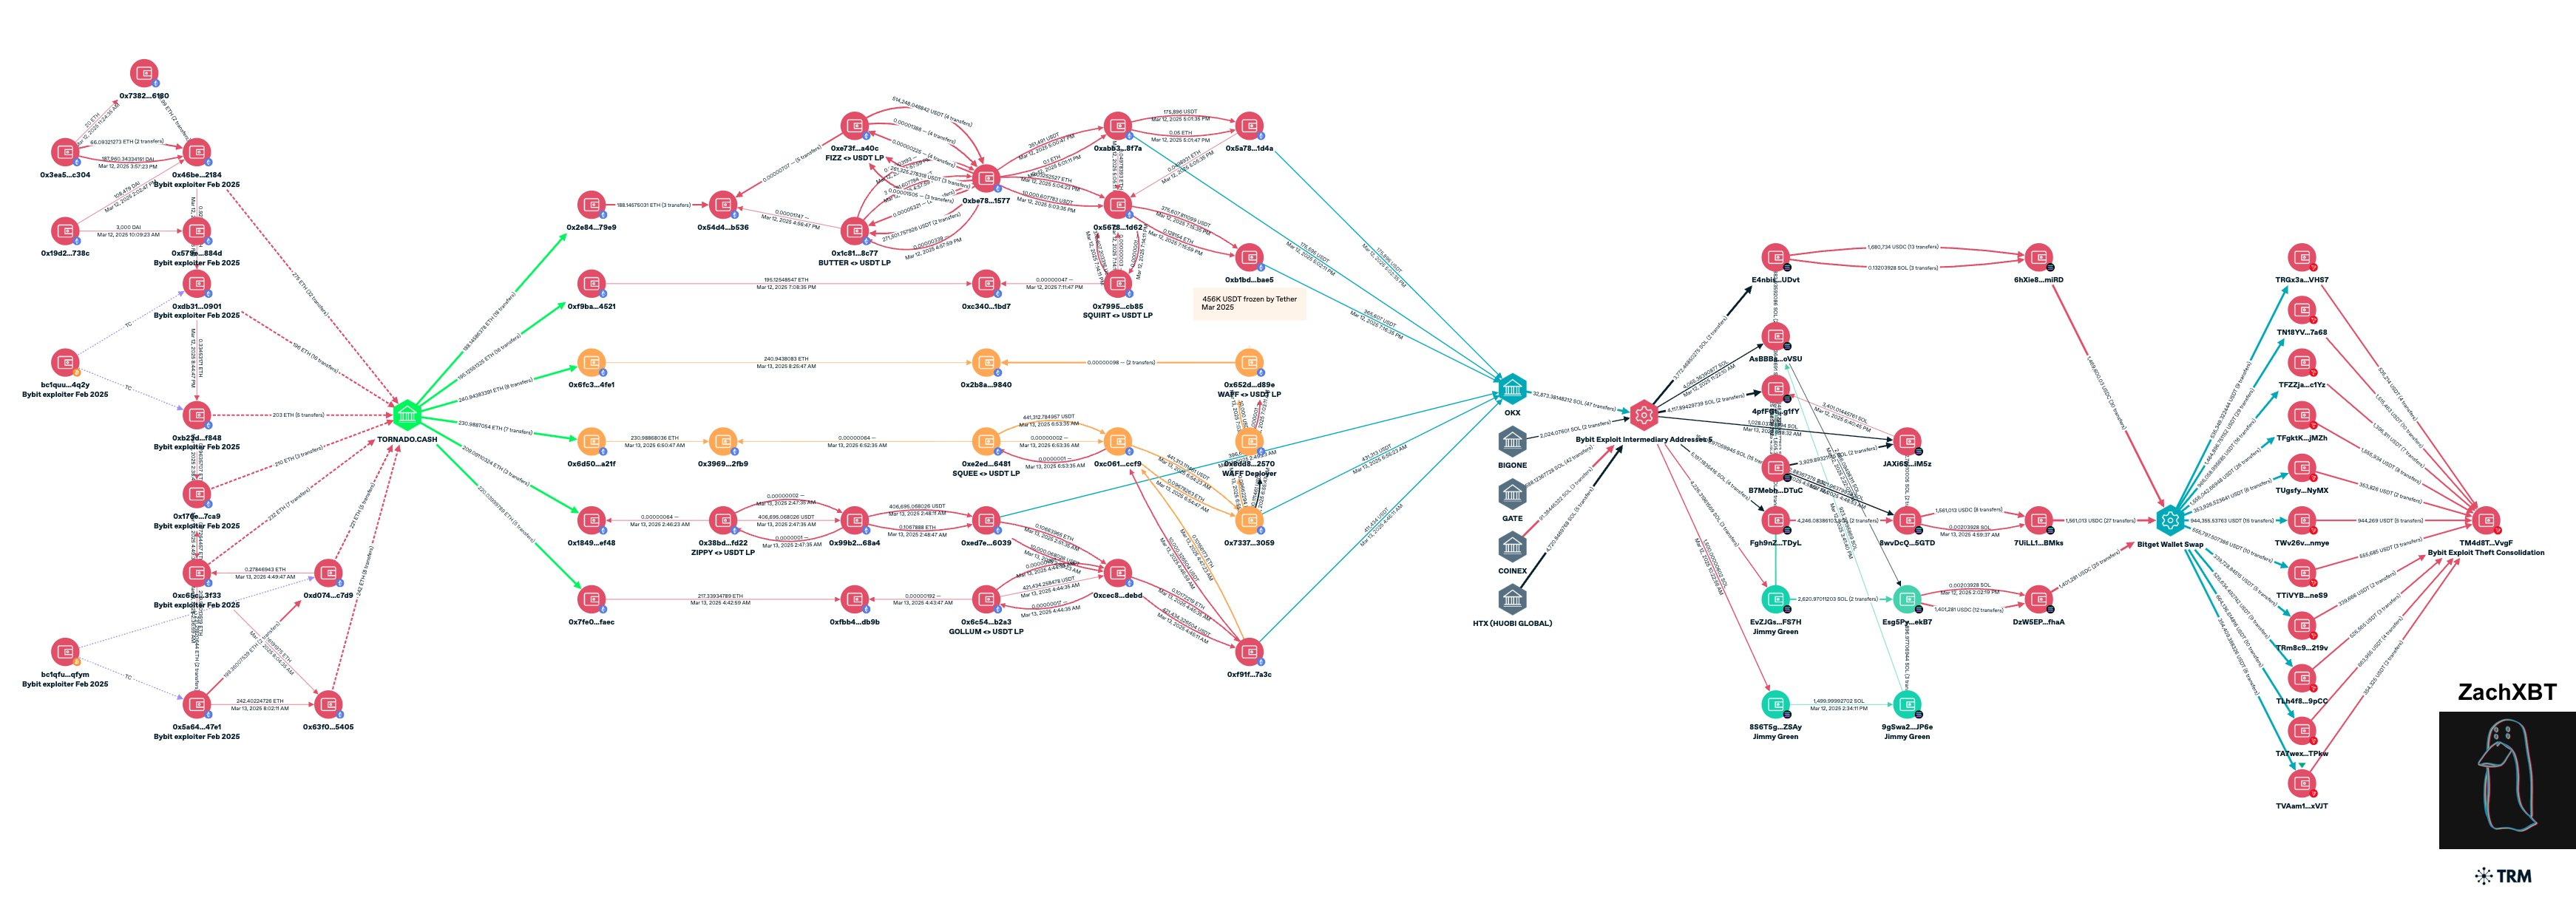
ZachXBT does not explain the mechanics in detail, so what follows is the general principle of such schemes rather than a description of specific transactions. An illiquid token has no market other than the pool controlled by the launderer himself. He creates a token, sets up a pool paired with USDT and runs a series of swaps and liquidity operations through it. At the end, the stolen money looks like pool income or proceeds from selling the token. No one checks the price of such a token, so almost any amount can be pushed through the pool. To analytics this looks like ordinary liquidity activity, and the link to the source becomes indirect.
For exchanges, the last part of the route is what matters: USDT that passed through such pools arrived at the deposit addresses of major platforms.
Crypto mixers: how they work and what their trace in a wallet history means3 Eyl 2026Devamını oku
Poloniex and Huione: traces of other cases
Jimmy talked about more than Bybit, and ZachXBT checked these stories as well.
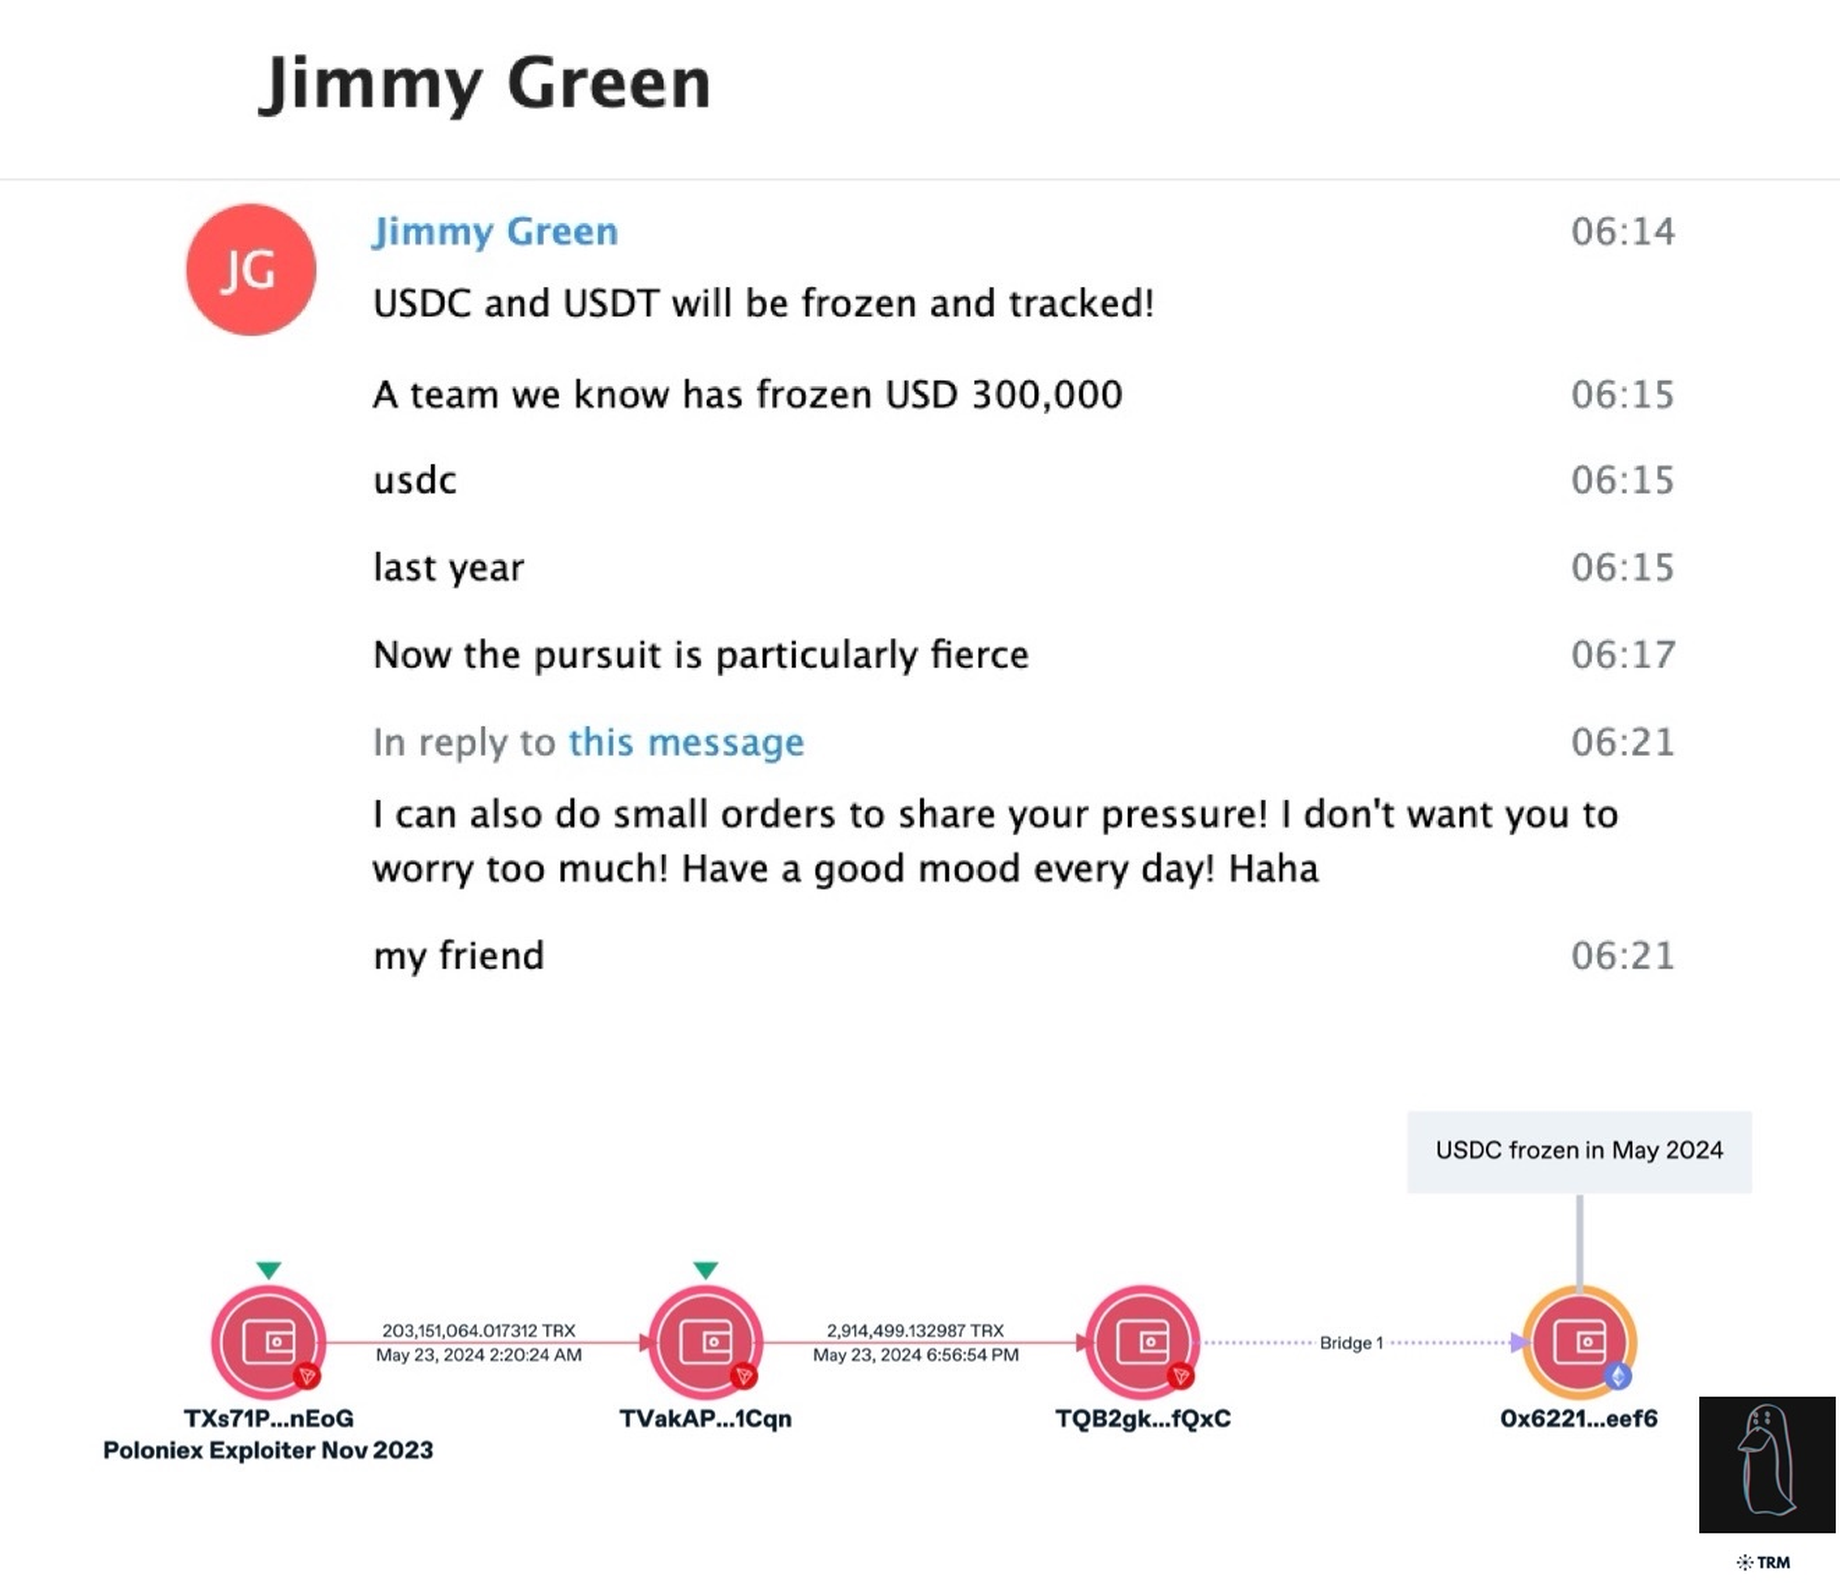
Poloniex. Jimmy mentioned that a team he knew had about $300,000 in USDC frozen the previous year. ZachXBT found that freeze on-chain: it was in fact 332,000 USDC from the hack of the Poloniex exchange, frozen in May 2024. The hack itself took place in November 2023, when around $126 million was stolen from hot wallets, and it is also attributed to Lazarus Group. On ZachXBT's graph the money moved from the Poloniex exploiter's address through several TRON addresses and a bridge to the address where the USDC was frozen. Jimmy himself commented: «USDC and USDT will be frozen and tracked! Now the pursuit is particularly fierce».
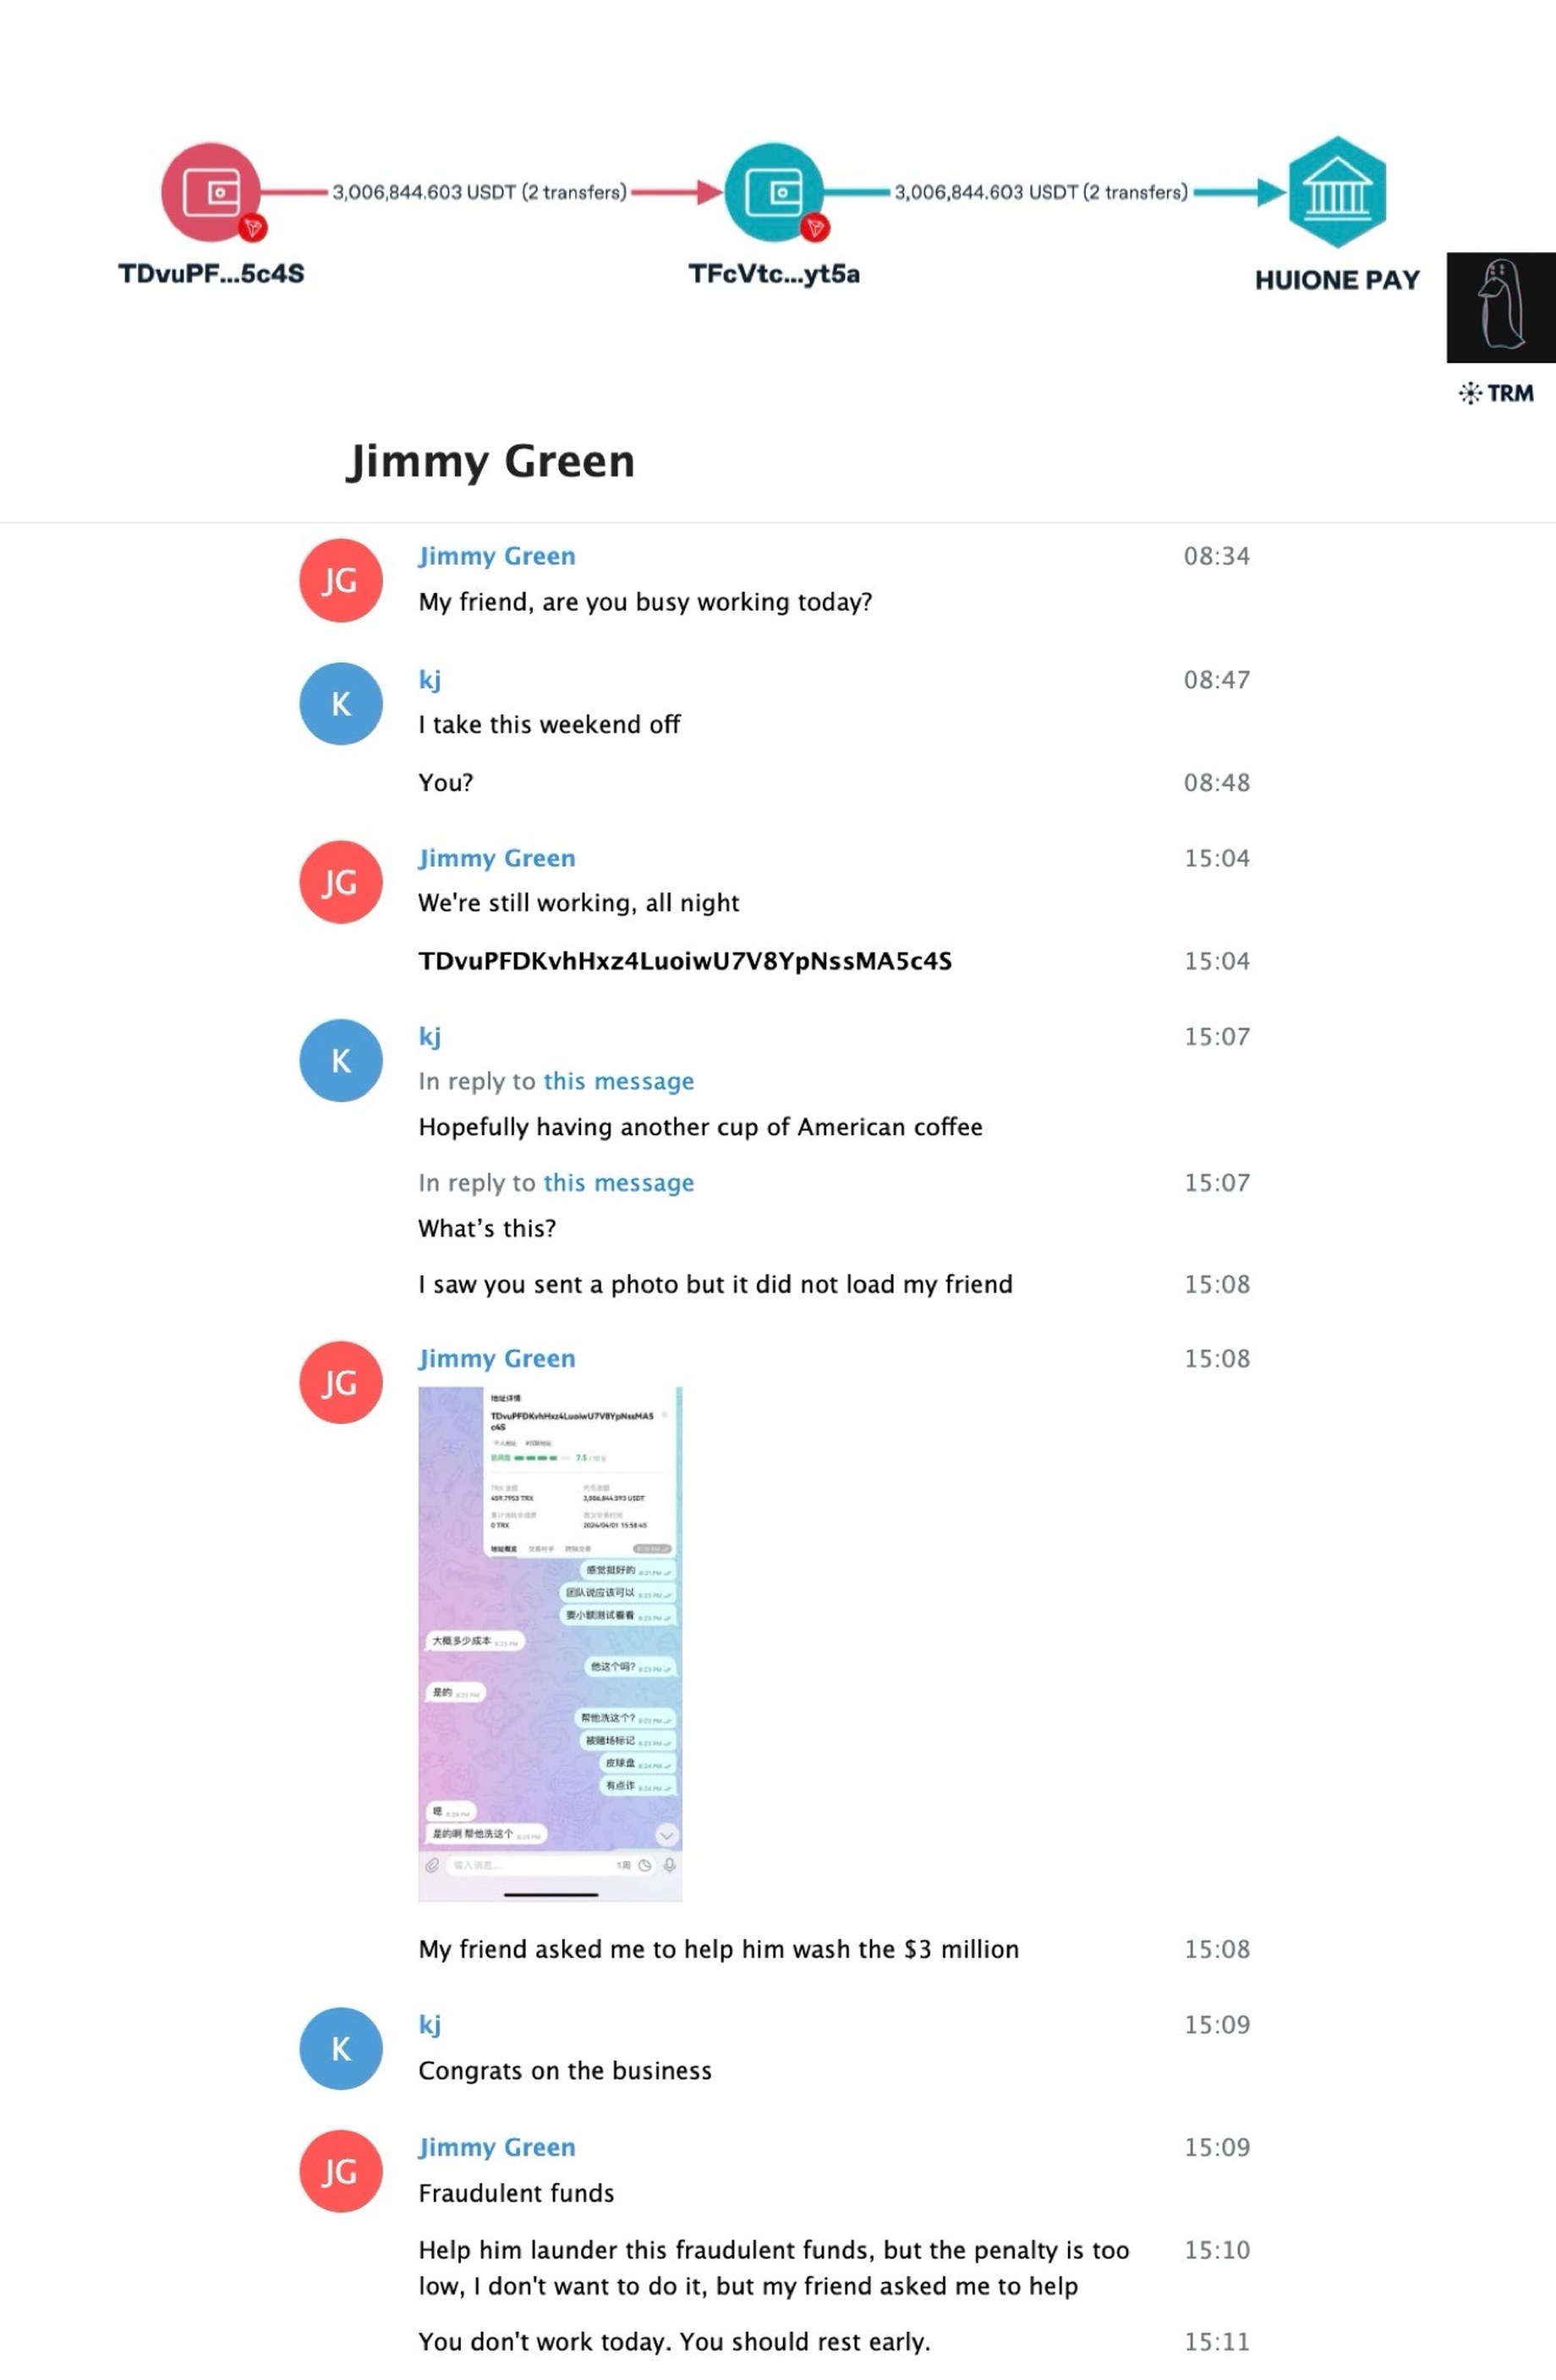
Huione Guarantee. Jimmy also mentioned laundering $3 million in fraud proceeds for another client. He sent the address TDvuPFDKvhHxz4LuoiwU7V8YpNssMA5c4S and complained that «the penalty is too low», apparently meaning his fee, but said a friend had asked him to help. ZachXBT traced the money to a Huione Guarantee hot wallet: on his graph, 3,006,844 USDT passes in two transfers through an intermediate address to a wallet labeled Huione Pay. According to Elliptic, this is the largest known shadow marketplace on Telegram, where services for scammers, stolen data and laundering were sold. It later rebranded as Haowang Guarantee. FinCEN designated Huione Group a primary money laundering concern and barred US financial institutions from dealing with it, and in April 2026 the former chairman of Huione Group, Li Xiong, was extradited from Cambodia to China on money laundering charges.
This link shows that Jimmy's group worked not only for North Korean hackers. The money of fraud victims went through the same infrastructure.
Mahjong, hunting and «killed pigs»: small talk between trades
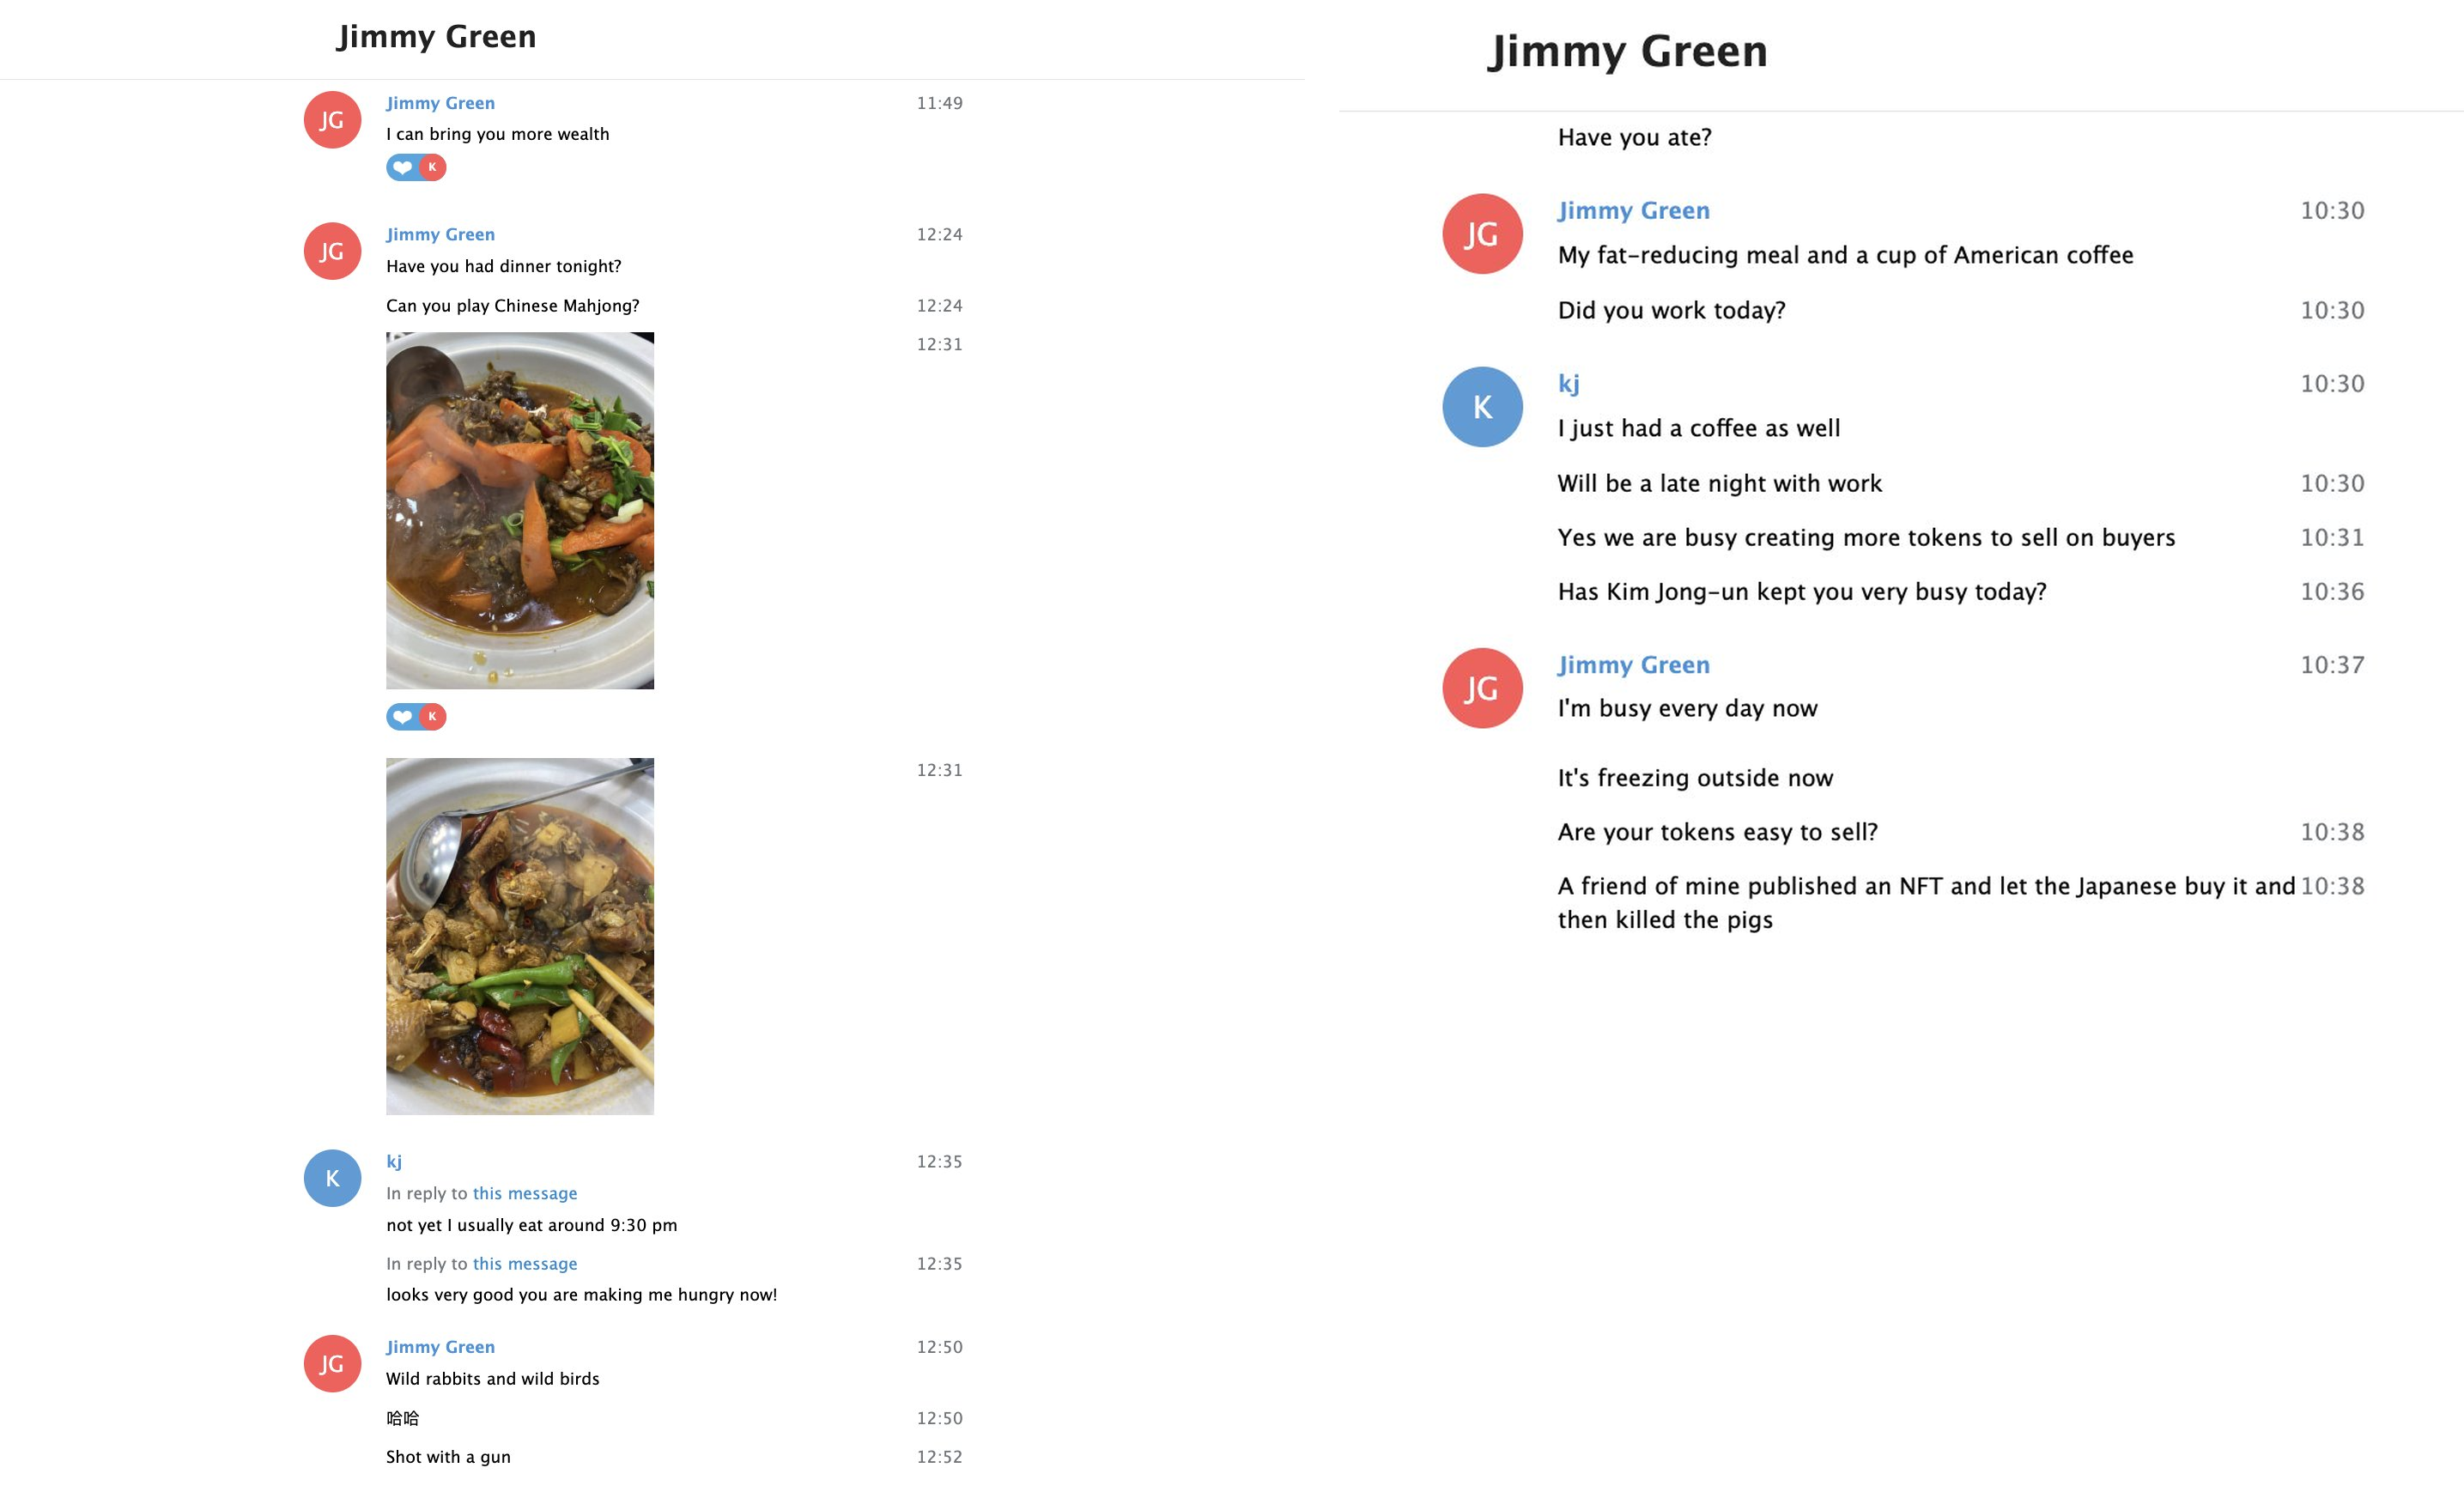
In between discussing laundering for North Korea, Jimmy talked a lot about his life: Chinese mahjong, wild rabbits and wild birds «shot with a gun», food, his «fat-reducing meal» and American coffee, family life and vacations at Disney. ZachXBT attributes Jimmy's awkward English to the use of a translator.
In these conversations ZachXBT kept up his cover: he wrote that his team was «busy creating more tokens to sell on buyers», posing as someone behind scam tokens. In response, Jimmy told him about a friend who «published an NFT and let the Japanese buy it and then killed the pigs». This is an almost literal translation of the Chinese slang 杀猪盘, «pig butchering», the name of a well-known fraud scheme.
Chinese OTC traders: not the first such case
It has long been known that North Korean hackers cash out through Chinese intermediaries. What is new in this story is the inside detail.
Jimmy describes his group as operating in Hong Kong and mainland China, exactly where the previously sanctioned traders worked. The scheme is the same: hackers steal, protocols like THORChain swap assets between networks, and Chinese OTC groups turn them into stablecoins and then, through acceptors, into fiat.
What is confirmed and what is still only the launderer's word
In investigations like this, it is important to separate verifiable data from the claims of the people involved.
| Claim | Source | Status |
|---|---|---|
| Jimmy's address received gas from a wallet linked to the Bybit hack | blockchain, public Bybit blacklist | confirmed on-chain |
| Jimmy's screenshot matches a THORChain order | THORChain explorer, transaction hash | confirmed on-chain |
| Jimmy's Solana addresses lead to a cluster with $12M+ in Bybit funds | blockchain | confirmed on-chain |
| Tether froze 442,000 USDT from this cluster (456,000 on the graph) | blockchain, freeze address | confirmed on-chain, amounts differ |
| Freeze of 332,000 USDC from the Poloniex hack | blockchain | confirmed on-chain |
| $3M in fraud proceeds went to Huione Guarantee | blockchain, ZachXBT's graph | confirmed on-chain according to ZachXBT |
| The group laundered more than $1 billion across several hacks | ZachXBT's estimate | not officially confirmed |
| Jimmy's team laundered most of the $1.5 billion from Bybit | Jimmy's words | ZachXBT says it is consistent with the patterns but did not quantify it |
| «Internal cooperation» with Tether and address monitoring | Jimmy's words | no confirmation |
There are no official charges against Jimmy Green or his group as of publication. ZachXBT writes that he immediately shared his findings with trusted investigators in the private sector and with the law enforcement agencies assigned to the case. He could not publish them sooner because of the sensitivity of the investigation.
What the investigation cost
ZachXBT put in $349,700 of his own money and lost a 5% fee on every order, with no guarantee that Jimmy would not disappear with the funds. He describes the personal risk of dealing with such a group as unknown. By his account, since 2022 he has helped freeze more than $75 million in connection with North Korea-related incidents. He funds his work through grants from foundations and donations.
What this means for exchanges, OTC desks and ordinary users
This is a story about North Korean hackers, but the consequences affect the whole market.
First, coins from such schemes do not stay inside the shadow economy. Acceptors sell the USDT on, and it can end up in the wallet of an ordinary P2P seller, a merchant or an OTC desk. If the issuer freezes an address that such funds passed through, or an exchange sees the link to the source, the problems land on the last holder.
Second, services like Jimmy's group openly advertise themselves on Telegram.
Third, checking a counterparty's address works against such schemes as well. The address 0xbaa5, to which Jimmy asked for money to be sent, was linked to a wallet on the Bybit blacklist through gas, meaning through a single transaction. This is visible before you send or accept anything.
You can check an address on KYTme: one report shows the scores of three providers – Crystal Intelligence, BitOK and VALEGA Chain Analytics.
Check an address
Siteyi ziyaret et